Implementing Cisco Enterprise Advanced Routing and Services (300-410 ENARSI) Exam Materials-Question 148 Discussion
Comment Image Comment Image Comment Image


Guidelines
This is a lab item in which tasks will be performed on virtual devices.

  1. Refer to the Tasks tab to view the tasks for this lab item.
  2. Refer to the Topology tab to access the device console(s) and perform the tasks.
  3. Console access is available for all required devices by clicking the device icon or using the tab(s) above the console window.
  4. All necessary preconfigurations have been applied.
  5. Do not change the enable password or hostname for any device.
  6. Save your configurations to NVRAM before moving to the next item.
  7. Click Next at the bottom of the screen to submit this lab and move to the next question.
  8. When Next is clicked, the lab closes and cannot be reopened.

Tasks
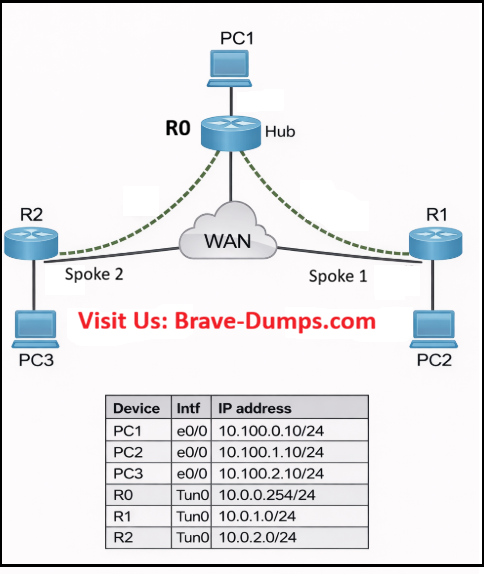
Configure IPSec security policy on tunnel interfaces to ensure data confidentiality and integrity where mGRE tunnels are up and running between HUB and SPOKE routers.

  1. Configure the ISAKMP policy parameters with the following attributes:
    AES256
    SHA256
    Group2
    lifetime 86400
  2. Ensure that GRE IP Header should be encrypted inside the IPSec packet. Verify IPSec security association and ISAKMP encrypted key. Use ISAKMP key "abc123".
  3. Configure a flexible ISAKMP Policy on the HUB to add peers that have the dynamic IP addresses where SPOKES must add HUB IP static entry using an encrypted key. Use a single command to configure it. Use IPSec phase-2 transform-set name as 'T-SET' and IPSec Profile name as 'IPSEC-PROFILE'.
ANSWER
 

A: R0:

 
R0>en
R0#config t
R0(config)#crypto isakmp policy 10
R0(config-isakmp)#encr aes 256
R0(config-isakmp)#hash sha256
R0(config-isakmp)#authentication pre-share
R0(config-isakmp)#group 2
R0(config-isakmp)#lifetime 86400
R0(config-isakmp)#exit
R0(config)#crypto isakmp key abc123 address 0.0.0.0
R0(config)#crypto ipsec transform-set T-SET esp-aes 256 esp-sha256-hmac
R0(cfg-crypto-trans)#mode tunnel
R0(cfg-crypto-trans)#exit
R0(config)#crypto ipsec profile IPSEC-PROFILE
R0(ipsec-profile)#set transform-set T-SET
R0(ipsec-profile)#exit
R0(config)#interface Tunnel0
R0(config-if)#tunnel protection ipsec profile IPSEC-PROFILE
R0(config-if)#ip nhrp map multicast dynamic
R0(config-if)#end
R0#wr
 

R1/R2:

 
Router>en
Router#config t
Router(config)#crypto isakmp policy 10
Router(config-isakmp)#encr aes 256
Router(config-isakmp)#hash sha256
Router(config-isakmp)#authentication pre-share
Router(config-isakmp)#group 2
Router(config-isakmp)#lifetime 86400
Router(config-isakmp)#exit
Router(config)#crypto isakmp key abc123 address 10.0.0.254
Router(config)#crypto ipsec transform-set T-SET esp-aes 256 esp-sha256-hmac
Router(cfg-crypto-trans)#mode tunnel
Router(cfg-crypto-trans)#exit
Router(config)#crypto ipsec profile IPSEC-PROFILE
Router(ipsec-profile)#set transform-set T-SET
Router(ipsec-profile)#exit
Router(config)#interface Tunnel0
Router(config-if)#tunnel protection ipsec profile IPSEC-PROFILE
Router(config-if)#end
Router#wr
(Invalid number of answers)

  • A.
  • B.
  • C.
  • D.
Correct Answer:

Brave-Dump Clients Votes


Comments


Anonymous User 2026-10-23 16:12:04

Selected Answers: No answers selected


I tried it on my LAB I encounter error:

*Oct 23 13:01:29.853: %CRYPTO-6-IKMP_MODE_FAILURE: Processing of Informational mode failed with peer at 115.14.56.2

I used DMVPN phase 1 and my issue is on the crypto isakmp key, I used the tunnel HUB IP. Then I change it to public IP of HUB and then the IPSec work.

can you please confirm if I am correct or wrong.

Thank you