View all questions & answers for the FCSS - Network Security 7.4 Support Engineer Exam Materials exam
FCSS - Network Security 7.4 Support Engineer Exam Materials - Question #21 Discussion
Community Explanations & Comments (1)
Brave-Dumps.com Admin
1 year ago
Selected: D
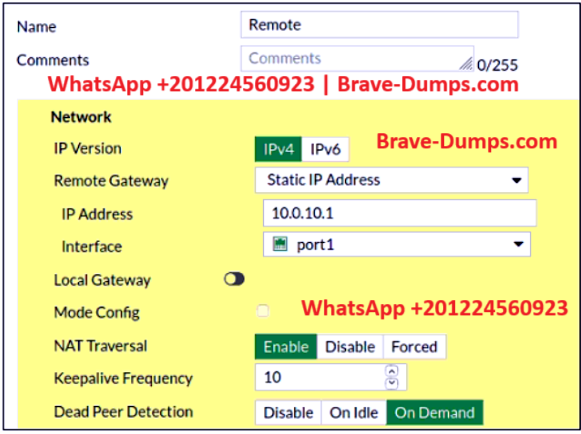
"The diagnose command is filtering for traffic on port 500, but with NAT Traversal enabled, IKE negotiations use port 4500 instead."
So there is no output
So there is no output
Refer to the exhibit, which contains a screenshot of some phase 1 settings. The VPN is up. To monitor traffic flow, the administrator enters the following CLI commands on an SSH session on FortiGate. However, the sniffer does not show any output. Why? (Choose one answer)
Brave-Dump Community Votes