View all questions & answers for the FCSS - SD-WAN 7.4 Architect Exam Materials exam
FCSS - SD-WAN 7.4 Architect Exam Materials - Question #23 Discussion
Community Explanations & Comments (3)
Brave-Dumps.com Admin
1 year ago
Selected: D
As per FCSS - SD-WAN 7.4 Architect Study Guide page: 190
Jonathan
1 year ago
Selected: B
Auxiliary sessions prevent dirty flags and has nothing to do with SD-WAN self Healing, the answer should be B
Brave-Dumps.com Admin
1 year ago
Dear Jonathan, D is the correct as per sd-wan 7.4 study guide page 190
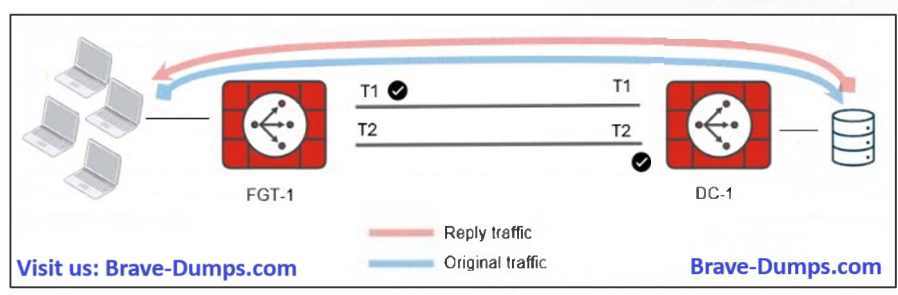
If you enable auxiliary sessions on both FortiGate devices in the previous topology, FGT-2 can now route the reply traffic through the best performing member...
please check it, you can download the study guide from: https://brave-dumps.com/study-and-lab-guides
Jonathan
1 year ago
Selected: D
You are tottaly right, thanks Omar
The administrator analyzed the traffic between a branch FortiGate and the server located in the data center, and noticed the behavior shown in the diagram. When the LAN clients located behind FGT1 establish a session to a server behind DC-1, the administrator observes that, on DC-1, the reply traffic is routed over T2, even though T1 is the preferred member in the matching SD-WAN rule. What can the administrator do to instruct DC-1 to route the reply traffic through the member with the best performance? (Choose one answer)
Brave-Dump Community Votes