View all questions & answers for the FCSS - SD-WAN 7.4 Architect Exam Materials exam
FCSS - SD-WAN 7.4 Architect Exam Materials - Question #40 Discussion
Community Explanations & Comments (3)
michael
1 year ago
Selected: C
confusing question. why not A. it matches source/destination. maybe gateway is not correct. Then it will match service3. C should be correct. Last match is D with perfect source/designation match. But top down approach will match service 3 before 4. any other logic ?
Brave-Dumps.com Admin
1 year ago
Dear michael, please check my comment.
Brave-Dumps.com Admin
1 year ago
Selected: D
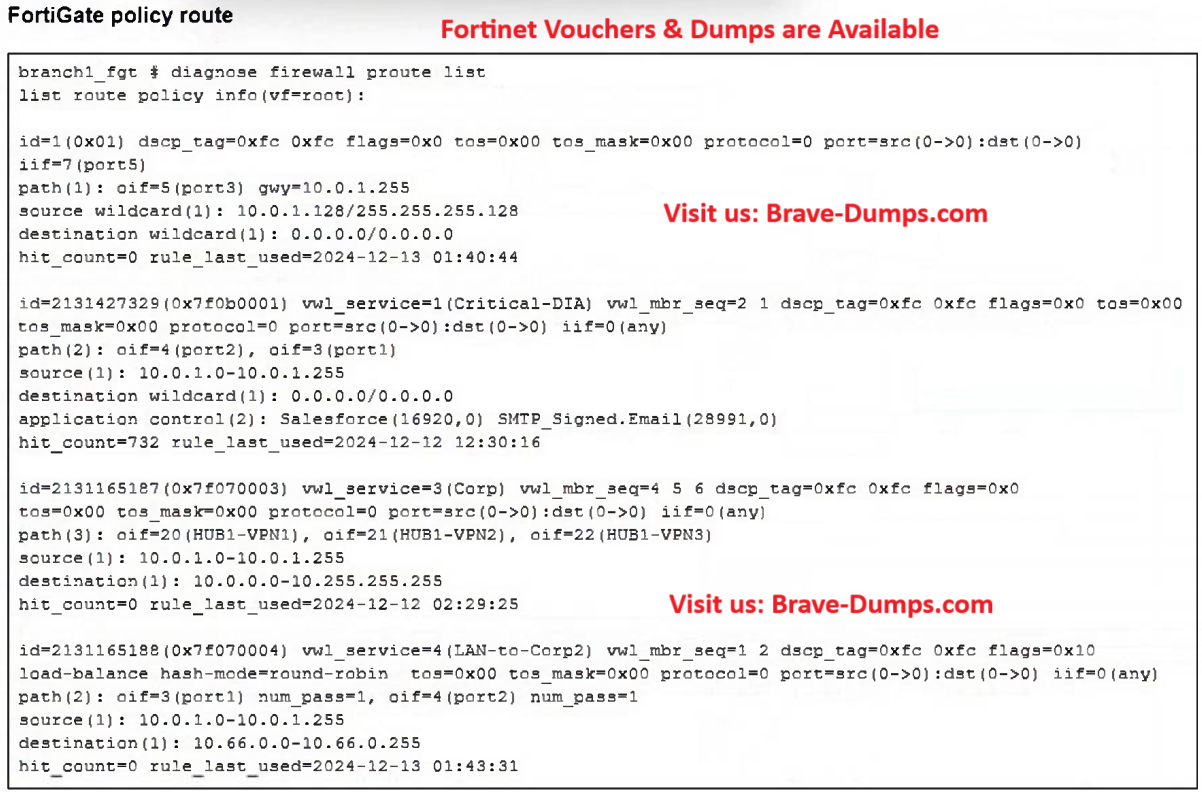
D is the correct and logical answer:
The source IP 10.0.1.133 and destination 10.66.0.125 are a perfect match for the last policy (service=4), both ranges match exactly.
This policy (service=4) uses SD-WAN members 1 and 2 with round-robin, so FortiGate will follow that logic.
Other options:
A: Doesn’t match — source subnet in that rule is 10.0.1.128/25, which doesn’t include 10.0.1.133.
B: Port2 is part of another rule (service=1) with extra application control (Salesforce/SMTP_Signed.Email), which likely doesn’t apply here.
C: Source matches, but the destination is too broad (0.0.0.0/0) — less specific than the last rule. In top-down matching, more specific match wins, even if it comes later.
So, while service=3 comes before service=4, it’s not a better match — that's why FortiGate hits the last rule instead.
FortiGate always uses the first rule that fully matches source and destination most accurately, and in this case, that’s D.
michael
1 year ago
A. 10.0.1.133 is in range 10.0.1.128/25, but seems gateway is same range as source subnet.
C. it matches top to bottom in SDWAN rules. this I have tested in the lab. just fyi.
Mattia Bruno
1 year ago
It's D but because of 2131427329, in this you can see it's for member 2or1 which are the same as the last one. and it's the only one with hit count
Elrasheed
1 year ago
Selected: D
D. is correct: Source and destination match and the only policy with hit_count greater than 0. Other rules has hit_count=0.
Refer to the exhibit. What conclusions can you draw about the traffic received by FortiGate originating from the source LAN device 10.0.1.133 and destined for the company's SMTP mail server at 10.66.0.125? (Choose one answer)
Brave-Dump Community Votes