View all questions & answers for the FCSS - SD-WAN 7.4 Architect Exam Materials exam
FCSS - SD-WAN 7.4 Architect Exam Materials - Question #51 Discussion
Community Explanations & Comments (4)
Pavol KUCHAR
1 year ago
Selected: C
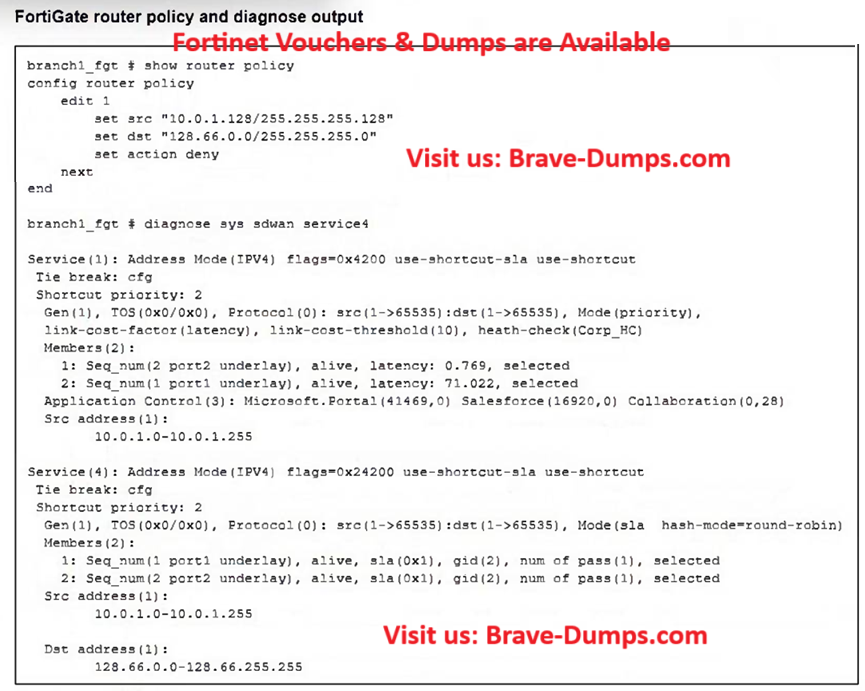
If the policy route action is deny (drop), the traffic is dropped immediately.
The traffic never reaches the SD-WAN rule processing phase.
The traffic never reaches the SD-WAN rule processing phase.
Brave-Dumps.com Admin
1 year ago
Good comment, Thanks Pavol!
Mattia Bruno
1 year ago
In the policy route deny is NOT drop but Stop Policy Routing. So FIB then A
Carlos Navarro
1 year ago
Selected: A
A. FortiGate routes the traffic flow according to the FIB. pg. 163.
Mattia Bruno
1 year ago
Selected: A
A page 163
Daniel
1 year ago
Selected: C
It' s C
When action deny is on policy route, indicate that FortiGate have to stop checking the firewall policies routes, but not drop the packet. Just check another entry routes like: Static route, OSP, BGP, SDWAN....
In this case, action is deny, then FortiGate check sdwan services, so its C
When action deny is on policy route, indicate that FortiGate have to stop checking the firewall policies routes, but not drop the packet. Just check another entry routes like: Static route, OSP, BGP, SDWAN....
In this case, action is deny, then FortiGate check sdwan services, so its C
Daniel
1 year ago
policy routes, BGP, sdwan.. cant drop or stop traffic, that's the task of rule policy
Refer to the exhibit. How does FortiGate handle the traffic with the source IP 10.0.1.130 and the destination IP 128.66.0.125? (Choose one answer)
Brave-Dump Community Votes