View all questions & answers for the FCSS – SD-WAN 7.6 Architect Exam Materials exam
FCSS – SD-WAN 7.6 Architect Exam Materials - Question #36 Discussion
Community Explanations & Comments (4)
Brave-Dumps.com Admin
1 year ago
Selected: D
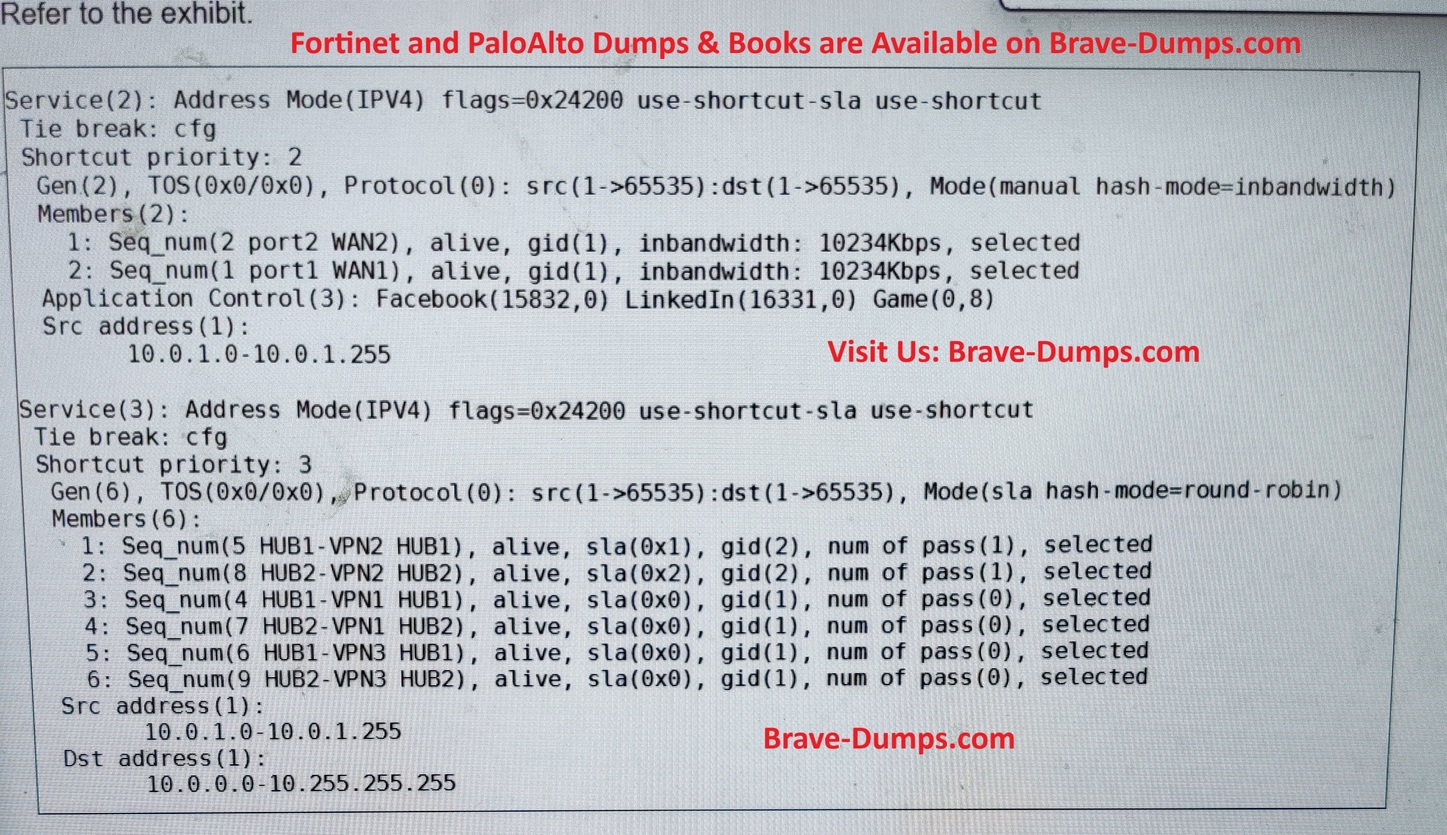
Src 10.0.1.124 (LAN) → Dst 10.0.0.254 (Corp) matches Service(3), which is mode SLA with hash-mode=round-robin and has six selected members: HUB1-VPN1/2/3 and HUB2-VPN1/2/3. With all links healthy, FortiGate load-balances new sessions across these tunnels—i.e., any interface in the HUB1 or HUB2 zones.
What do you think?
What do you think?
Marcelo cechinel
11 months ago
Selected: B
Strategy: sla hash-mode=round-robin. This means that traffic will be distributed (balanced) among the members that are currently active (alive) and passing the SLA (number of passes > 0).
Only the HUB1-VPN2 and HUB2-VPN2 interfaces are meeting the SLA.
Only the HUB1-VPN2 and HUB2-VPN2 interfaces are meeting the SLA.
Salon Raj Joshi
11 months ago
Selected: B
b is correct as sla is pass and hash mode is round robin
Praneeth Kalutarage
11 months ago
Selected: B
Both two interfaces paces sla and destination matches, first one is app based
Refer to the exhibit. The administrator configured two SD-WAN rules to load balance the traffic. Which interfaces does FortiGate use to steer the traffic from 10.0.1.124 to 10.0.0.254? (Choose one answer)
Brave-Dump Community Votes