View all questions & answers for the FCSS – SD-WAN 7.6 Architect Exam Materials exam
FCSS – SD-WAN 7.6 Architect Exam Materials - Question #43 Discussion
Community Explanations & Comments (3)
Gavin Romario
11 months ago
Selected: B
mode=round-robin
Brave-Dumps.com Admin
11 months ago
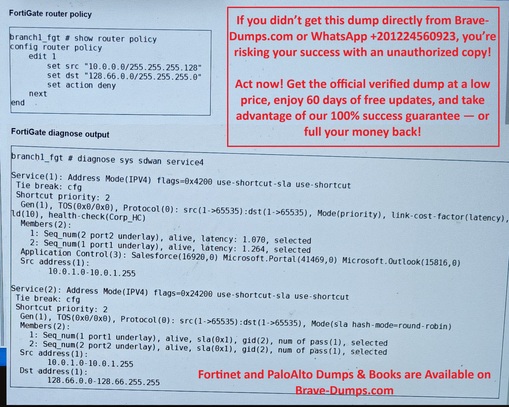
Although mode=round-robin is indeed configured in the SD-WAN settings, the SD-WAN rule will not be reached at all because the router policy above it already matches (even if its action is deny).
Therefore, FortiGate will not forward the traffic to SD-WAN, but instead falls back to the FIB (routing table).
Brave-Dumps.com Admin
11 months ago
Selected: A
On FortiGate, a policy route (PBR) configured with the action deny doesn’t actually drop the traffic.
Instead, it simply tells the system not to use that policy route. When this happens, the packet is handed back to the normal routing process — the FIB (Forwarding Information Base) — to determine where it should go next.
In this case:
- Source 10.0.1.130 matches 10.0.1.128/25
- Destination 128.66.0.125 matches 128.66.0.0/24
- The router policy says action = deny, meaning “skip this policy route.”
As a result, FortiGate reverts to the FIB for routing decisions rather than dropping the packet.
Moussaa
11 months ago
Hello,
But the route policy shows 10.0.0.0/25 witch does not match the source IP 10.0.1.130 (out of range). So for the me the answer is B
Sateesh
10 months ago
Selected: A
Correct Answer: A
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Info Aigles Mali
10 months ago
Could please let us know why response is A because as per the sdwan rule2, traffic will be load balanced between port 1 and port 2 ?
Refer to the exhibit. How does FortiGate handle the traffic with the source IP 10.0.1.130 and the destination IP 128.66.0.125? (Choose one answer)
Brave-Dump Community Votes