View all questions & answers for the Implementing and Operating Cisco Security Core Technologies v1.1 (350-701 SCOR v1.1) Exam Materials exam
Implementing and Operating Cisco Security Core Technologies v1.1 (350-701 SCOR v1.1) Exam Materials - Question #313 Discussion
Community Explanations & Comments (1)
Brave-Dumps.com Admin
3 months ago
Selected: C
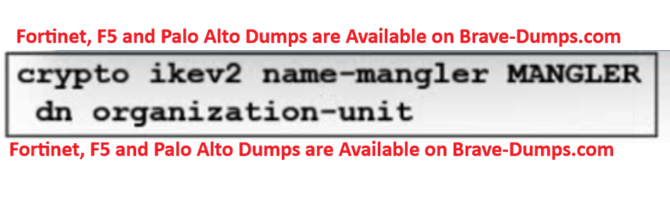
The match identity certificate command in an IKEv2 authorization policy specifies which certificate attribute should be used to match the peer against the policy. In this case, the policy checks the Organizational Unit (OU) field and expects its value to be MANGLER.
Therefore, when an IKEv2 peer presents a certificate whose OU attribute is set to MANGLER, the router uses that value to evaluate the authorization policy. If the certificate identity matches the policy criteria, the IKEv2 security association can be established successfully.
Therefore, when an IKEv2 peer presents a certificate whose OU attribute is set to MANGLER, the router uses that value to evaluate the authorization policy. If the certificate identity matches the policy criteria, the IKEv2 security association can be established successfully.
Refer to the exhibit. An engineer is implementing a certificate based VPN. What is the result of the existing configuration? (Choose one answer)
Brave-Dump Community Votes