View all questions & answers for the Implementing and Operating Cisco Security Core Technologies v1.1 (350-701 SCOR v1.1) Exam Materials exam
Implementing and Operating Cisco Security Core Technologies v1.1 (350-701 SCOR v1.1) Exam Materials - Question #397 Discussion
Community Explanations & Comments (1)
HOSSAM ELDIN MOHAMED SA
3 months ago
Selected: D
D because we need dns server 1 to communicate with server 2
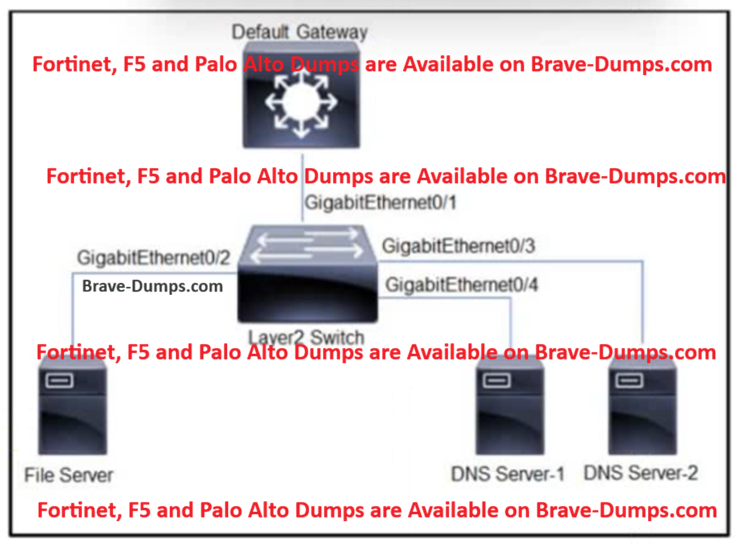
Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server? (Choose one answer)
Brave-Dump Community Votes