View all questions & answers for the MS Azure Administrator Associate (AZ-104) Exam Materials exam
MS Azure Administrator Associate (AZ-104) Exam Materials - Question #94 Discussion
Community Explanations & Comments (1)
Edward
2 months ago
Selected: D
Hi everyone, I think the provided answer (E) is incorrect. The correct answer should be D.
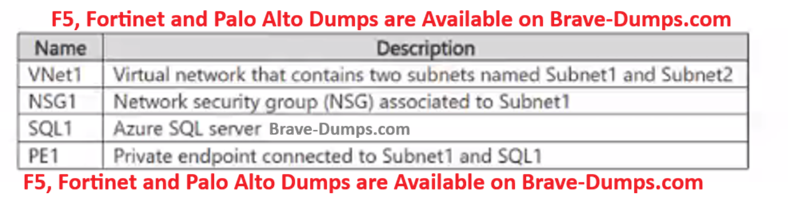
By default, Azure bypasses Network Security Group (NSG) rules for traffic directed to a Private Endpoint. To enforce NSG1 rules and restrict access to PE1, you must explicitly enable Network Policies for Private Endpoints on the subnet. A Service Endpoint is a completely different routing feature used to access PaaS public IPs.
Configuring it won't help the NSG filter traffic for the already existing Private Endpoint.
Brave-Dumps.com Admin
2 months ago
Thanks
You have an Azure subscription that contains the resources shown in the following table. PE1 Private endpoint connected to Subnet1 and SQL1 You need to add a rule to NSG1 that will restrict network access to PE1. What should you do first? (Choose one answer)
Brave-Dump Community Votes