View all questions & answers for the NSE 4 - FortiOS 7.6 Administrator Exam Materials exam
NSE 4 - FortiOS 7.6 Administrator Exam Materials - Question #20 Discussion
Community Explanations & Comments (12)
MOHAMED IBRAHIM ELHADI AHMED
1 year ago
Selected: D
Refer to guide
javaughn Bryan
1 year ago
Selected: D
its D....strict SNI must match with the CN AND SAN...if not..the connect will close
Miroslaw Lerch
1 year ago
Selected: C
FortiGate Study Guide (SSL Inspection Section)
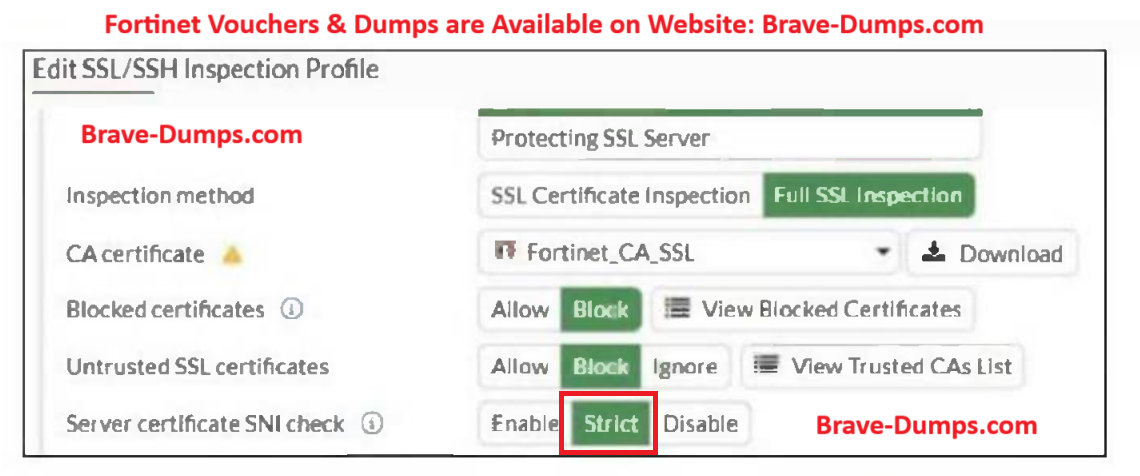
“When the Server certificate SNI check configuration is Enable, FortiGate uses the domain in the CN field instead of the domain in the SNI field if the domain in the SNI field does not match any of the domains listed in the CN and SAN fields. With Strict, FortiGate closes the client connection if there is a mismatch. When SNI check is Disable, FortiGate always rates URLs based on the FQDN.”
Key Clarifications (Direct from Study Guide):
Enable: FortiGate falls back to the certificate’s CN when the SNI doesn’t match the certificate’s CN or SAN values.
Strict: FortiGate closes the connection immediately if SNI does not match either CN or SAN.
Disable: FortiGate ignores SNI and makes URL decisions solely on the FQDN.
Alessandro
1 year ago
Selected: C
C is correct
Mazzonetto
1 year ago
Selected: D
When the Server certificate SNI check configuration is Enable, FortiGate uses the domain in the CN field
instead of the domain in the SNI field if the domain in the SNI field does not match any of the domains listed in
the CN and SAN fields. With Strict, FortiGate closes the client connection if there is a mismatch. When SNI
check is Disable, FortiGate always rates URLs based on the FQDN.
instead of the domain in the SNI field if the domain in the SNI field does not match any of the domains listed in
the CN and SAN fields. With Strict, FortiGate closes the client connection if there is a mismatch. When SNI
check is Disable, FortiGate always rates URLs based on the FQDN.
Mazzonetto
1 year ago
Correct : C
chiras theodoros
11 months ago
Selected: C
Server certificate SNI Check options
Strict: Closes the connection if the SNI in the client's hello message does not match the CN or SAN fields in the server's certificate.
Enable: Checks the SNI against the CN/SAN. If there is a mismatch, it uses the CN in the server certificate to perform URL filtering instead of closing the connection.
Disable: Does not perform the SNI check. FortiGate will always use the FQDN from the server certificate for URL rating, even if the SNI was different.
Mohamed
11 months ago
Selected: D
Guide
imade
11 months ago
Selected: C
page 263
Miguel
10 months ago
Selected: C
strict SNI must match with the CN or SAN, You are not required, when creating a certificate, to put the same name in the CN (Common Name) as in the SAN (Subject Alternative Name). So as long as it is in one of the two, it would be enough. It is ridiculous to require it to be in both. The only thing is to verify both fields
Vic Geek
10 months ago
Selected: C
Page 287 of the 7.6 Study Guide shows that its CN or SAN
Anonymous User
9 months ago
Selected: C
C because if one of the 2 has a mismatch it will close the connection
Check the SNI in the hello message with the CN or SAN field in the returned server certificate:
Strict: If it is mismatched, close the connection.
Check the SNI in the hello message with the CN or SAN field in the returned server certificate:
Strict: If it is mismatched, close the connection.
Ahmed El Hasseen El Tom El Shaikh Berair
3 months ago
Selected: C
20
Refer to the exhibit. What would be the impact of these settings on the Server certificate SNI check configuration on FortiGate? (Choose one answer)
Brave-Dump Community Votes