View all questions & answers for the NSE 4 - FortiOS 7.6 Administrator Exam Materials exam
NSE 4 - FortiOS 7.6 Administrator Exam Materials - Question #40 Discussion
Community Explanations & Comments (4)
Thomas Pfaff
10 months ago
Selected: C
This feels like a poor question to me...it would make more sense if the question was "How can the Deny policy be adjusted to allow Remote_User2 to still access other portions of the network while still blocking access to the Webserver" or something
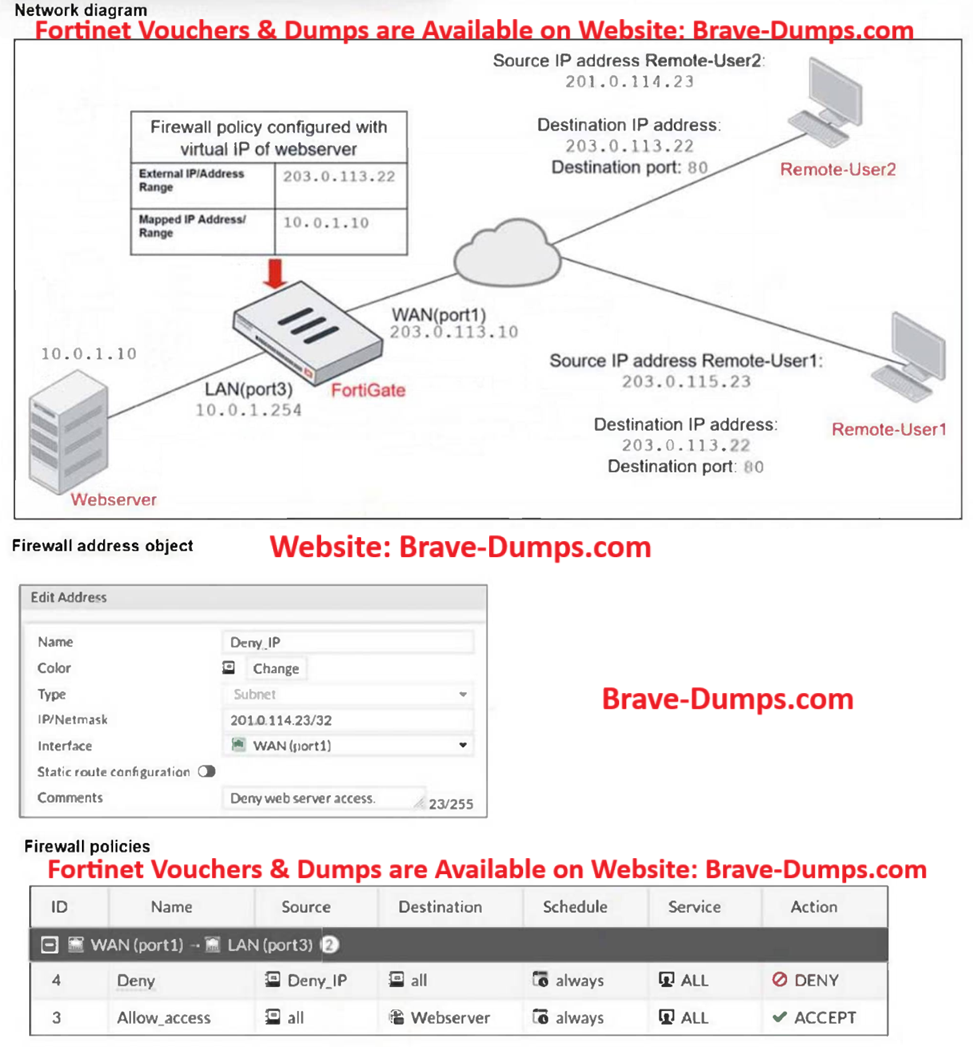
Right now the question is asking what ADDITIONAL configuration can be done to block access to the Webserver from RU-2, but there doesn't need to be any additional configuration, the "all" dst is already denying access
Right now the question is asking what ADDITIONAL configuration can be done to block access to the Webserver from RU-2, but there doesn't need to be any additional configuration, the "all" dst is already denying access
Anonymous User
6 months ago
Selected: C
correct is c
Ahmed El Hasseen El Tom El Shaikh Berair
3 months ago
Selected: C
40
AHMAD ALRAMADAN
1 month ago
is it correct ?
Anonymous User
3 months ago
Selected: C
You need to select VIP object to make rule working
Refer to the exhibits. The exhibits show a diagram of a FortiGate device connected to the network, and the firewall configuration. An administrator created a Deny policy with default settings to deny Webserver access for Remote-User2. The policy should work such that Remote-User1 must be able to access the Webserver while preventing Remote-User2 from accessing the Webserver. Which additional configuration can the administrator add to a deny firewall policy, beyond the default behavior, to block Remote-User2 from accessing the Webserver? (Choose one answer)
Brave-Dump Community Votes