View all questions & answers for the NSE 4 - FortiOS 7.6 Administrator Exam Materials exam
NSE 4 - FortiOS 7.6 Administrator Exam Materials - Question #68 Discussion
Community Explanations & Comments (5)
Ashequr Rahman Khan
7 months ago
Selected: A
Please explain why the source address will not be changed to 10.0.11.254? Is it because NAT is disabled in Web_Server_Access(2) policy?
abdulrahman
7 months ago
yes the source wont change because of Source NAT disabled in policy 2.
abdulrahman
7 months ago
Selected: D
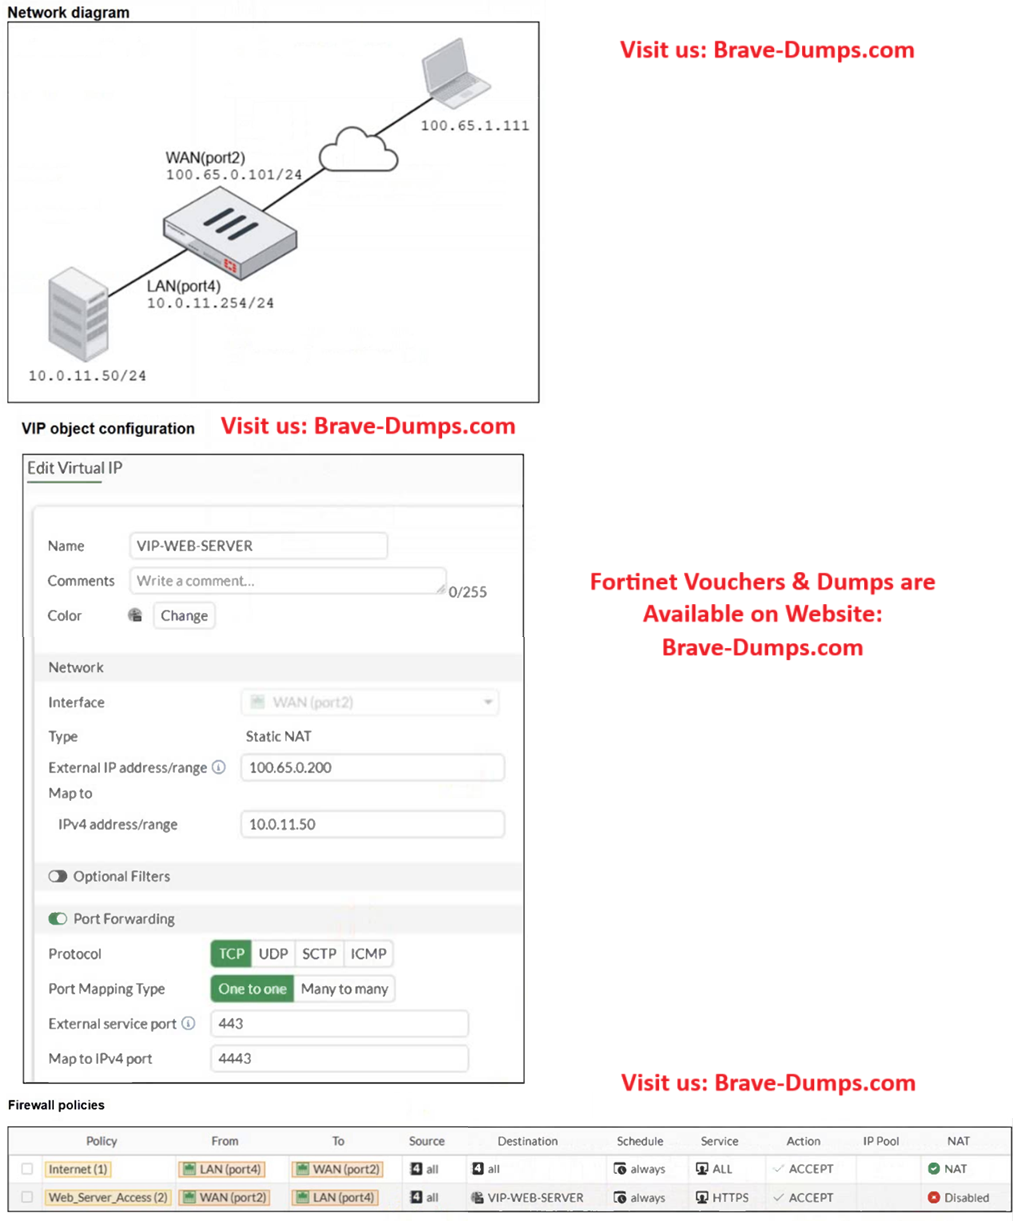
policy NAT affect the Source address while the Virtual IP mapping act as destination NAT and affect the destination and has nothing to do with the NAT being disabled in the policy because the mapping happen before applying the policy.
onder
7 months ago
Selected: D
second policy will be applied.
Ahmed El Hasseen El Tom El Shaikh Berair
3 months ago
Selected: D
68
[email protected]
2 weeks ago
Selected: D
NAT is disabled from WAN to LAN policy, so SRC 100.65.1.111
VIP address static NAT. so DST i10.0.11.50 and DPORT redirected from 443 to 4443
VIP address static NAT. so DST i10.0.11.50 and DPORT redirected from 443 to 4443
Refer to the exhibits. A diagram of a FortiGate device connected to the network VIP object and firewall policy configurations are shown. The WAN (port2) interface has the IP address 100.65.0.101/24. The LAN (port4) interface has the IP address 10.0.11.254/24. If the host 100.65.1.111 sends a TCP SYN packet on port 443 to 100.65.0.200, what will the source address, destination address, and destination port of the packet be at the time FortiGate forwards the packet to the destination? (Choose one answer)
Brave-Dump Community Votes