View all questions & answers for the NSE 5 - FortiWeb 8.0 Administrator Exam Materials exam
NSE 5 - FortiWeb 8.0 Administrator Exam Materials - Question #64 Discussion
Community Explanations & Comments (1)
Ahmed
1 day ago
Selected: B
B
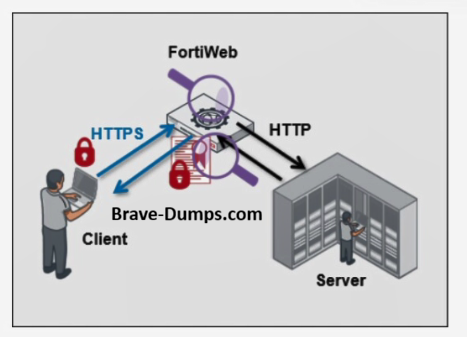
Refer to the exhibit. You are configuring SSL offloading on FortiWeb to protect a public-facing application. Clients connect using HTTPS, while FortiWeb forwards requests to the back-end server using HTTP. You are reviewing certificate deployment and need to decide where to install the private key for the certificate used in client connections. In this SSL offloading setup, which device is responsible for using the private key associated with the web server certificate? (Choose one answer)
Brave-Dump Community Votes