View all questions & answers for the NSE 6 - FortiEDR 7.0 Administrator Exam Materials exam
NSE 6 - FortiEDR 7.0 Administrator Exam Materials - Question #12 Discussion
Community Explanations & Comments (3)
Brave-Dumps.com Admin
6 months ago
Selected: D
Explanation — Why this answer?
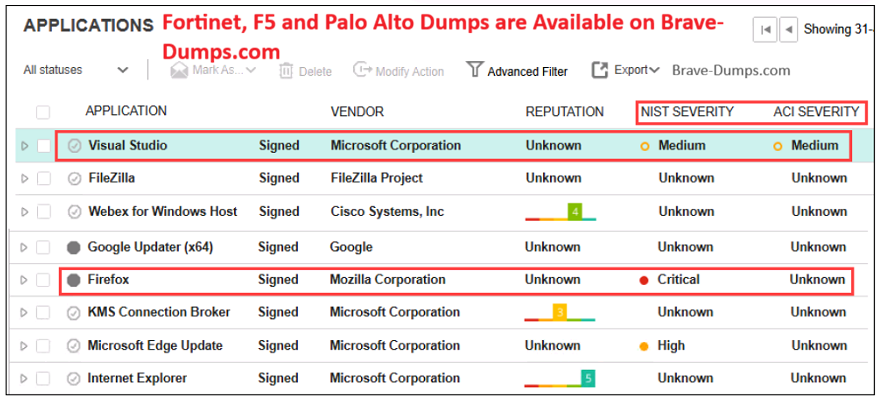
The ACI (Adversary Capability Intelligence) metric in FortiEDR indicates whether a vulnerability is actively being exploited in the wild.
A Medium severity vulnerability with confirmed active exploitation (ACI) is more urgent than a Critical vulnerability with no known exploitation (ACI: Unknown).
Therefore, Visual Studio (Medium NIST, Medium ACI) should be prioritized over Firefox (Critical NIST, ACI Unknown) because it represents a real, active threat, not just a theoretical risk.
Anonymous User
6 months ago
Selected: D
Correct answer: D
Anonymous User
5 months ago
Selected: D
• ACI Severity—Adversary Centric Intelligence (ACI) rating provided by FortiRecon leveraging FortiGuard Threat Analysts to provide comprehensive coverage of dark web, open source, and technical threat intelligence, including threat actor insights. This information enables administrators to proactively assess risks, respond faster to incidents, better understand their attackers, and protect assets. Unlike NIST that is a technical risk score context; ACI is a real-time actor behavior and intent context.
https://docs.fortinet.com/document/fortiedr/7.2.3/administration-guide/255973/severity#:~:text=Component%20registration%20in%20a%20multi,files%20modification%20activity%20is%20blocked
https://docs.fortinet.com/document/fortiedr/7.2.3/administration-guide/255973/severity#:~:text=Component%20registration%20in%20a%20multi,files%20modification%20activity%20is%20blocked
Refer to the Exhibit: A FortiEDR analyst is prioritizing response efforts. One application has a vulnerability score of Critical but an Unknown ACI rating, while another has a Medium vulnerability score with active ACI evidence of adversary targeting. Which application must be addressed first? (Choose one answer)
Brave-Dump Community Votes