View all questions & answers for the NSE 6 - FortiEDR 7.0 Administrator Exam Materials exam
NSE 6 - FortiEDR 7.0 Administrator Exam Materials - Question #13 Discussion
Community Explanations & Comments (3)
Brave-Dumps.com Admin
6 months ago
Selected: C
Explanation — Why this answer?
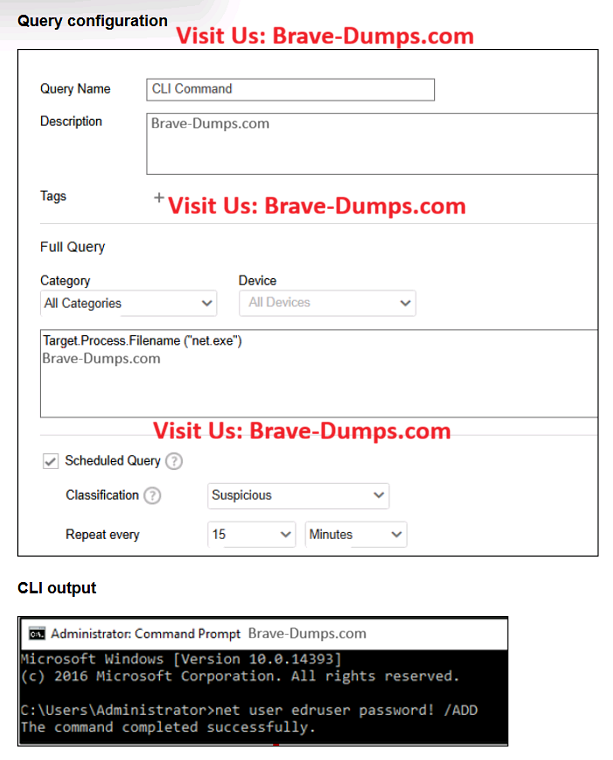
The query is configured with Target.Process.Filename = “net.exe” as the matching criterion and a classification set to “Suspicious”, scheduled to run every 15 minutes in FortiEDR.
When net.exe is executed, the scheduled query detects the process and generates an incident classified as “Suspicious.”
By default, FortiEDR does not block CLI commands, so the action results in detection and alerting, not prevention.
Anonymous User
6 months ago
Selected: C
C
The query generates an incident only when net.exe is detected matching the condition, not automatically for every CLI execution
The query generates an incident only when net.exe is detected matching the condition, not automatically for every CLI execution
Anonymous User
5 months ago
Selected: C
• No playbooks are associated to the query so no actions will be done upon matching the query such as blocking the command
Refer to the exhibits. What happens when the net user command runs on an endpoint? (Choose one answer)
Brave-Dump Community Votes