View all questions & answers for the NSE 6 - FortiEDR 7.0 Administrator Exam Materials exam
NSE 6 - FortiEDR 7.0 Administrator Exam Materials - Question #33 Discussion
Community Explanations & Comments (3)
Brave-Dumps.com Admin
6 months ago
Selected: C, D
Explanation — Why this answer?
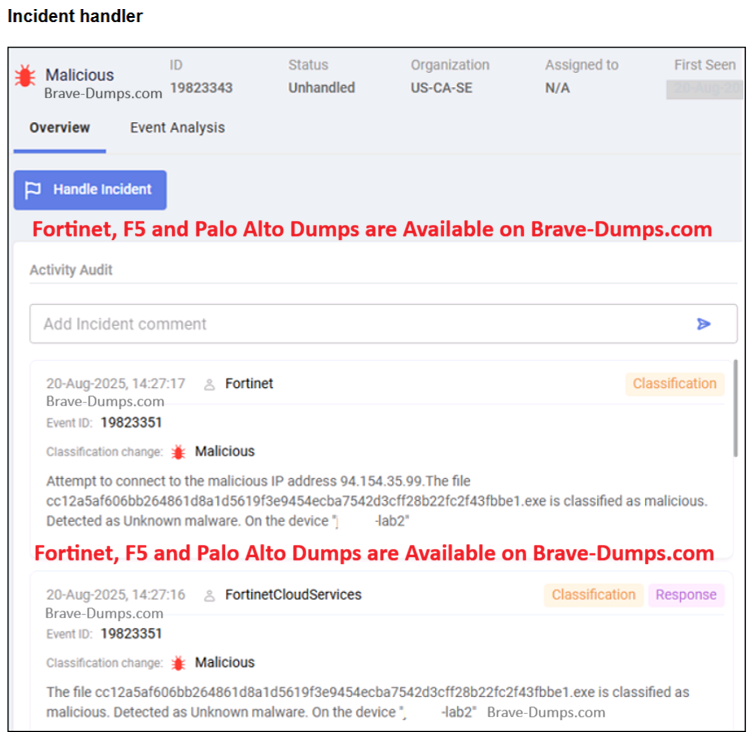
Fortinet Cloud Services (FCS) clearly classified the file as “Malicious” in the activity log. The note “Detected as Unknown malware” indicates that FortiEDR had never encountered this malware before. The status is “Unhandled,” meaning the incident has not been resolved. The classification is “Malicious,” not “Suspicious.”
Fortinet Cloud Services (FCS) clearly classified the file as “Malicious” in the activity log. The note “Detected as Unknown malware” indicates that FortiEDR had never encountered this malware before. The status is “Unhandled,” meaning the incident has not been resolved. The classification is “Malicious,” not “Suspicious.”
Anonymous User
5 months ago
Selected: C, D
CD
Anonymous User
5 months ago
Selected: C, D
FortiEDR shows that FortinetCloudServices (FCS) has clearly classified the file as “Malicious” in the activity log. The message “Detected as Unknown malware” indicates that FortiEDR had never previously encountered this malware.
The status is “Unhandled”, meaning the incident has not yet been resolved. The classification is “Malicious”, not “Suspicious”.
The status is “Unhandled”, meaning the incident has not yet been resolved. The classification is “Malicious”, not “Suspicious”.
Refer to the exhibit. Based on the exhibit, which two observations are true? (Choose two answers)
Brave-Dump Community Votes