View all questions & answers for the NSE 6 - FortiManager 7.6 Administrator Exam Materials exam
NSE 6 - FortiManager 7.6 Administrator Exam Materials - Question #13 Discussion
Community Explanations & Comments (3)
Saeed Abd El Halim Hamada
1 year ago
Selected: B, C
Correct Answer: B &C ,
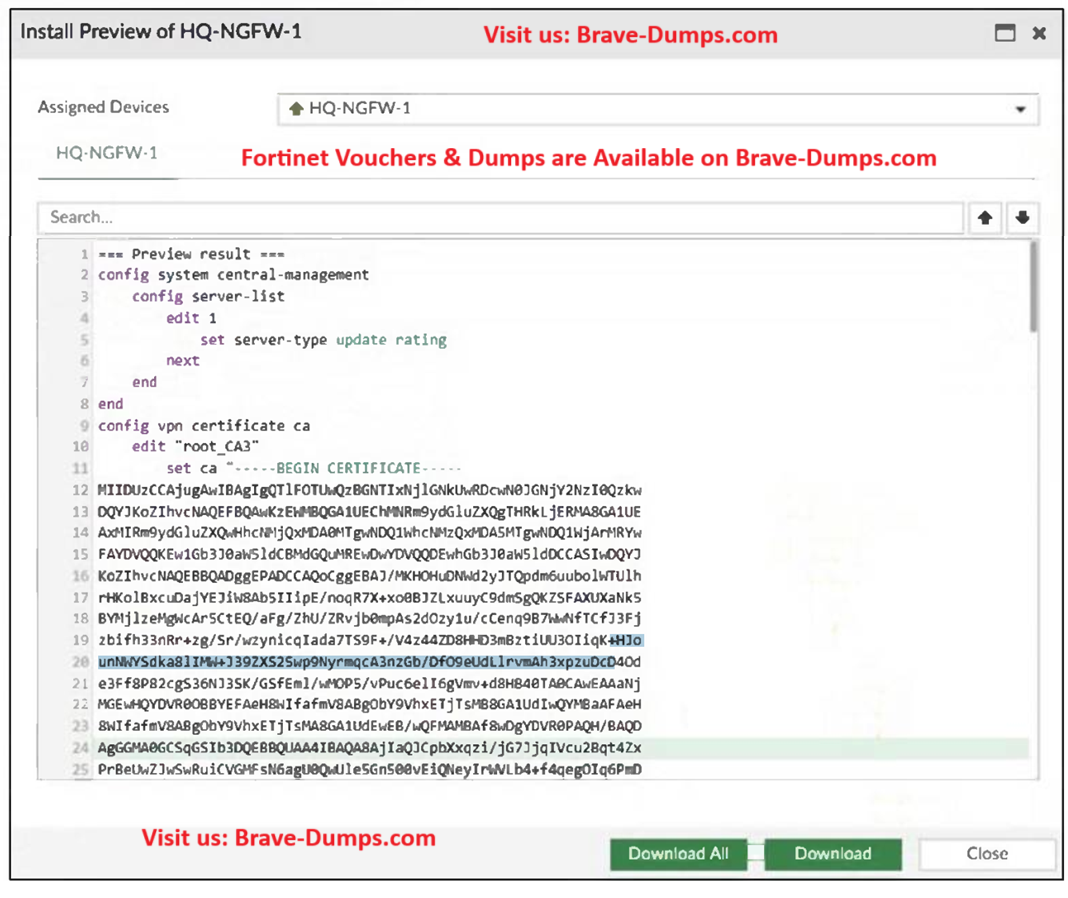
From this output
config vpn certificate ca
edit "root_CA3"
set ca "-----BEGIN CERTIFICATE-----"
This means the certificate "root_CA3" is being added to the FortiGate and can be used for SSL inspection, IPsec tunnels, or certificate-based authentication in policies or objects.
D. Incorrect — The config doesn’t show root_CA3 being used for FGFM authentication.
Mahboab Ali Ghaleb
1 year ago
Selected: B, D
CA certificates are not used directly in address objects or policy rules.
They are used for SSL inspection, certificate validation, or FortiManager-to-FortiGate trust.
They are used for SSL inspection, certificate validation, or FortiManager-to-FortiGate trust.
Alejandro Rivarola
9 months ago
Selected: B, D
usa la the CA certificate named root_CA3 para autenticar el fortigate con el manager.
y usa al manager como servidor de actualizacion del fortiguard
y usa al manager como servidor de actualizacion del fortiguard
Refer to the exhibit. An administrator assigned a new policy package to FortiGate HQ-NGFW-1. In the installation preview, they noticed some settings they did not modify and are unsure about the changes. Based on the exhibit, which two things will happen if they continue with the installation? (Choose two answers)
Brave-Dump Community Votes