View all questions & answers for the NSE 6 - FortiSIEM 7.2 Analyst Exam Materials exam
NSE 6 - FortiSIEM 7.2 Analyst Exam Materials - Question #11 Discussion
Community Explanations & Comments (2)
mahmoud mostafa
1 year ago
Selected: A
Group by is some how like the filter.
just enhance how to show the result.
while the real restrictive condition is the aggregation.
if the event happens more than 3 times show me ,, else i am not interested
just enhance how to show the result.
while the real restrictive condition is the aggregation.
if the event happens more than 3 times show me ,, else i am not interested
kair ahmid
1 year ago
Selected: C
I think is C
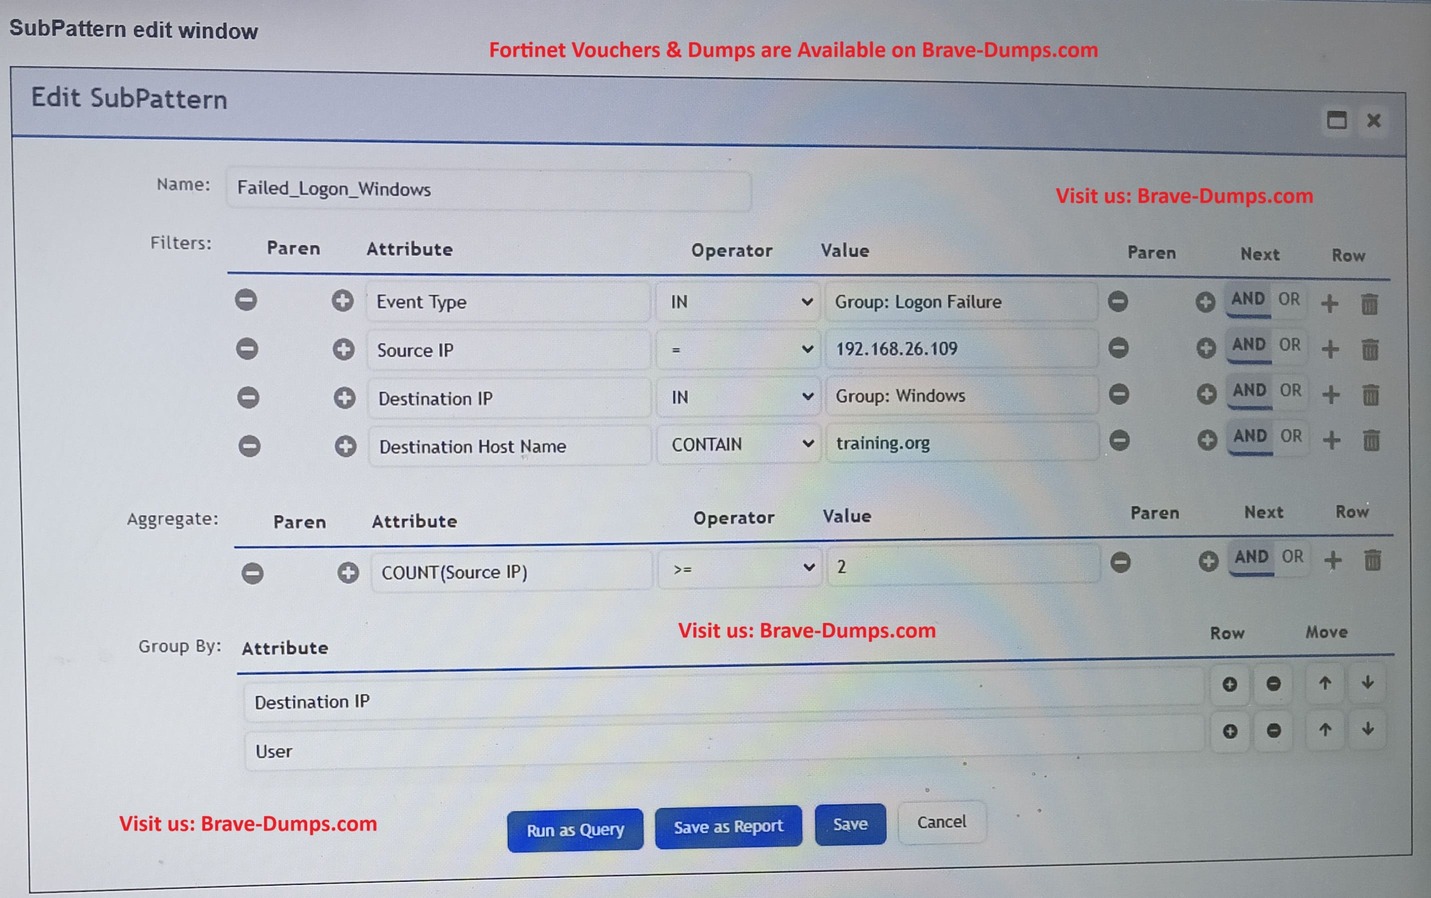
By grouping on Destination IP and User, the rule only counts events that share the same pair of values. Even though the filters match events in Analytics, they’re split across different groups, so COUNT(Source IP) >= 2 is never reached within a single group, and no incidents are generated.
By grouping on Destination IP and User, the rule only counts events that share the same pair of values. Even though the filters match events in Analytics, they’re split across different groups, so COUNT(Source IP) >= 2 is never reached within a single group, and no incidents are generated.
Refer to the exhibit. An analyst is troubleshooting the rule shown in the exhibit. It is not generating any incidents, but the filter parameters are generating events on the Analytics tab. What is wrong with the rule conditions? (Choose one answer)
Brave-Dump Community Votes