View all questions & answers for the NSE 6 - Network Security 7.6 Support Engineer Materials exam
NSE 6 - Network Security 7.6 Support Engineer Materials - Question #28 Discussion
Community Explanations & Comments (3)
Brave-Dumps.com Admin
1 year ago
Selected: C
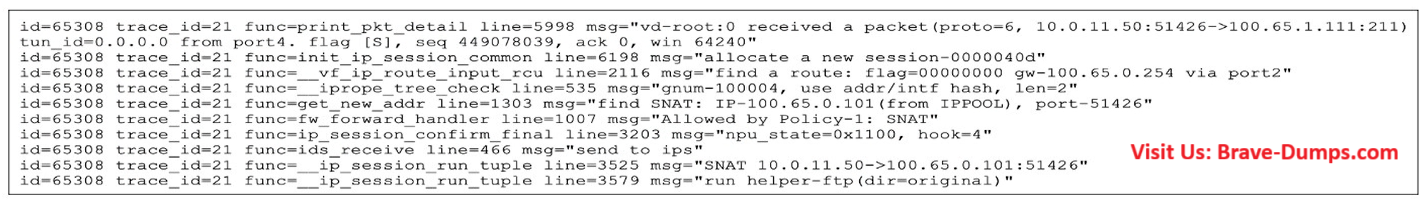
From the debug output that FortiGate triggered the FTP helper instead of using the proxy, which happens when the protocol isn’t mapped to the correct port (211) under Protocol Options, confirming that the FTP protocol hasn’t been mapped to port 211.
What do you think?
What do you think?
Anonymous User
6 months ago
Selected: C
Network_Security_Support_Engineer_7.6_Study_Guide Page 118
Anonymous User
4 months ago
Selected: A
Study guide page 274:
When a policy is set to proxy-based inspection, the settings in Protocol Options instruct the FortiGate to direct specified destination ports to their respective proxy process, except when ANY is set for an enabled protocol.
In this scenario, the FortiGate must send the traffic to the IPS engine to be processed by the CPU, in order to identify the protocol before directing it to the proxy process.
An administrator has configured a firewall policy to use proxy-based inspection mode. What could explain the messages observed in the debug flow output? (Choose one answer)
Brave-Dump Community Votes