View all questions & answers for the NSE 6 - Network Security 7.6 Support Engineer Materials exam
NSE 6 - Network Security 7.6 Support Engineer Materials - Question #45 Discussion
Community Explanations & Comments (5)
gerardo echeto
9 months ago
Selected: A, D
Why are A and D correct?
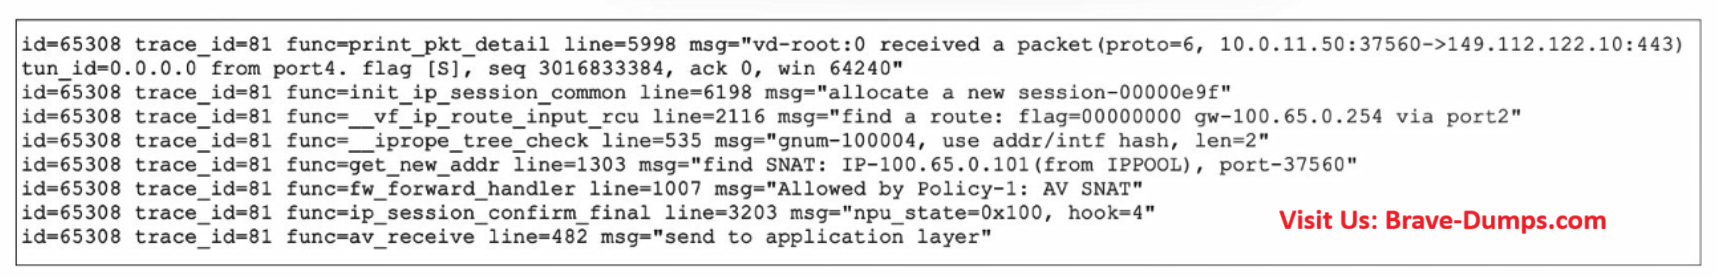
A (Web Filter in Proxy mode): The line `msg="send to application layer"` is irrefutable proof. Only when a profile (like the Web Filter) is in Proxy mode is traffic sent to the "Application Layer" (the WAD daemon).
D (Firewall Policy in Proxy mode): In current versions of FortiOS, for traffic to be sent to the application layer in this way, the firewall policy must be configured in Proxy Inspection Mode.
Why is C incorrect (even though it shows 0x100)?
Proxy-based = CPU.
Flow-based = NPU (Offload).
The value `npu_state=0x100` in this debug is a "false positive" for actual offload. It indicates that the software identified the session, but the subsequent `send to application layer` message overrides any hardware acceleration. The traffic remains on the CPU because the NPU cannot process proxies.
James
9 months ago
Selected: A, D
https://community.fortinet.com/t5/FortiGate/Technical-Tip-Reasons-why-the-session-is-not-offloaded-to-NPU/ta-p/336627
Reasons why the session is not offloaded to NPU
2. The firewall policy includes proxy-based security profiles.
3. Accepted by firewall policies that include proxy-based virus scanning, proxy-based web filtering, DNS filtering, DLP, Anti-Spam, VoIP, ICAP, Web Application Firewall, or Proxy options.
Reasons why the session is not offloaded to NPU
2. The firewall policy includes proxy-based security profiles.
3. Accepted by firewall policies that include proxy-based virus scanning, proxy-based web filtering, DNS filtering, DLP, Anti-Spam, VoIP, ICAP, Web Application Firewall, or Proxy options.
Mehdi
8 months ago
Selected: A, D
msg="send to application layer" this is proxy based inspection , for flow based you'd see send to ips so D is correct
Proxy-based inspection is required for certain web filter features (e.g., full URL rewriting, safe search enforcement in some modes), and the debug path confirms proxy handling so A
C : Incorrect because "send to application layer" means the traffic is processed by the proxy daemon (WAD), which runs on CPU
Mehdi
8 months ago
Selected: A, C
A : inspection mode (proxy-based vs. flow-based) is configured at the security profile level
C: If it were not offloaded, the trace would typically show npu state=0x0 (or 0x0 0x0), often with a no_ofld_reason
C: If it were not offloaded, the trace would typically show npu state=0x0 (or 0x0 0x0), often with a no_ofld_reason
Anonymous User
6 months ago
Selected: C, D
Option C
npu_state=0x100
This indicates the session is offloaded to the NP (Network Processor)
Option D
send to application layer
This is the key giveaway
Traffic is being forwarded to the application layer (proxy)
👉 This only happens when:
Proxy-based inspection mode is enabled on the firewall policy
✔ In flow-based mode:
Traffic stays in kernel fast path
You would NOT see “send to application layer”
Refer to the exhibit. Which two observations can you make about the web filter traffic captured using the flow tool? (Choose two answers)
Brave-Dump Community Votes