View all questions & answers for the NSE 6 - Network Security 7.6 Support Engineer Materials exam
NSE 6 - Network Security 7.6 Support Engineer Materials - Question #71 Discussion
Community Explanations & Comments (2)
Adam
9 months ago
Selected: A
Question seems invalid for FortiGate 7.6 where static route priority 0 is not supported anymore.
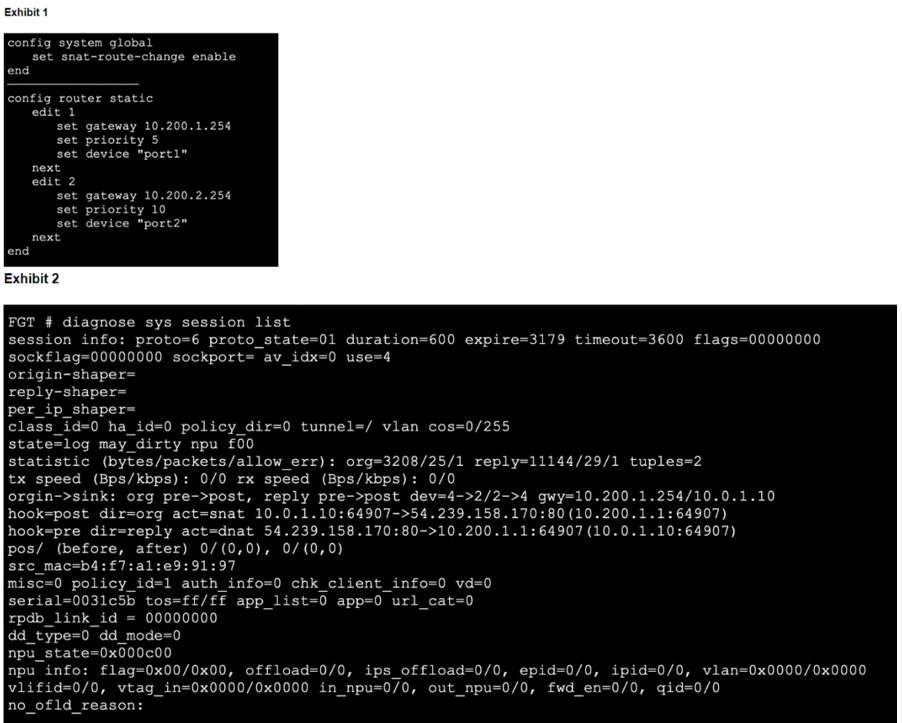
If it's meant for old version where priority 0 is supported and it's most preferred priority, then quoting Study Guide with snat-route-change enabled, "Note that during reevaluation of SNAT sessions, if the new route and firewall policy lookup results in a change of the SNAT IP address, then FortiGate drops the packet and clears the session. This means that the impacted application could have to initiate a new connection to resume network connectivity, especially if the application is TCP-based.", so A is a correct answer.
If it's meant for old version where priority 0 is supported and it's most preferred priority, then quoting Study Guide with snat-route-change enabled, "Note that during reevaluation of SNAT sessions, if the new route and firewall policy lookup results in a change of the SNAT IP address, then FortiGate drops the packet and clears the session. This means that the impacted application could have to initiate a new connection to resume network connectivity, especially if the application is TCP-based.", so A is a correct answer.
Anonymous User
6 months ago
Selected: A
Network_Security_Support_Engineer_7.6_Study_Guide Page 93 & 515
Refer to the exhibits, which show the configuration on FortiGate and partial session information for internet traffic from a user on the internal network. If the priority on route ID 2 were changed from 10 to 0, what would happen to traffic matching that user session? (Choose one answer)
Brave-Dump Community Votes