View all questions & answers for the NSE 6 - Network Security 7.6 Support Engineer Materials exam
NSE 6 - Network Security 7.6 Support Engineer Materials - Question #9 Discussion
Community Explanations & Comments (6)
Brave-Dumps.com Admin
1 year ago
Selected: A
We need another check from our expert clients. Anyone available to review it?
Mohammed Khaled
11 months ago
Selected: C
since it is phase 1 yet the answer is not correct, I believe C will be accurate as DH is not matching and the message showing no proposal chosen.
Pedro Joao Serafim Junior
10 months ago
Selected: A
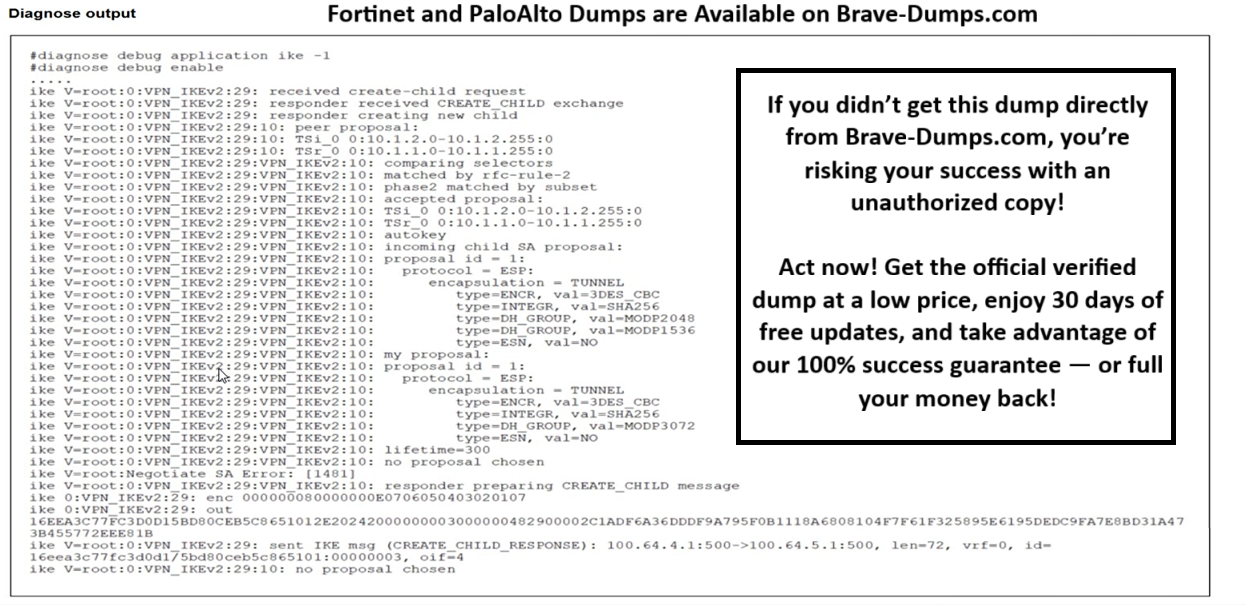
This a mismatch phase2 negotiation, the DHGroup is wrong.
Adam
9 months ago
Selected: C
Logs clearly show IPsec phase 2 PFS DH group mismatch (MOD2048/MOD1536 vs MOD3072) while there's match in encryption algorithm 3DES and hashing algorithm SHA256, any idea why C is wrong?
Brave-Dumps.com Admin
9 months ago
Selected: C
C is the correct one
Anonymous User
6 months ago
Selected: C
In Phase1 SA all 3 valuses are sent i.e. Encryption (3DES, AES etc), Integration/Hashing (SHA, SHA256 etc) and DH Group. In Pahes SA only has Encryption (3DES, AES etc), Integration/Hashing (SHA, SHA256 etc) and DH group is sent seprately when PFS is enabled and in debug you will clearly see PFS
diagnose debug application ike -1 is for Phse1 debug
Network_Security_Support_Engineer_7.6_Study_Guide Page 323
diagnose debug application ike -1 is for Phse1 debug
Network_Security_Support_Engineer_7.6_Study_Guide Page 323
Refer to the exhibit. An IPsec VPN tunnel using IKEv2 was brought up successfully, but when the tunnel rekey takes place the tunnel goes down. The debug command for IKE was enabled and, in the exhibit, you can review the partial output of the debug IKE while attempting to bring the tunnel up. What is causing the tunnel to be down? (Choose one answer)
Brave-Dump Community Votes