View all questions & answers for the NSE 6 – SD-WAN 7.6 Enterprise Administrator Exam Materials exam
NSE 6 – SD-WAN 7.6 Enterprise Administrator Exam Materials - Question #12 Discussion
Community Explanations & Comments (3)
Anonymous User
8 months ago
Selected: A, C
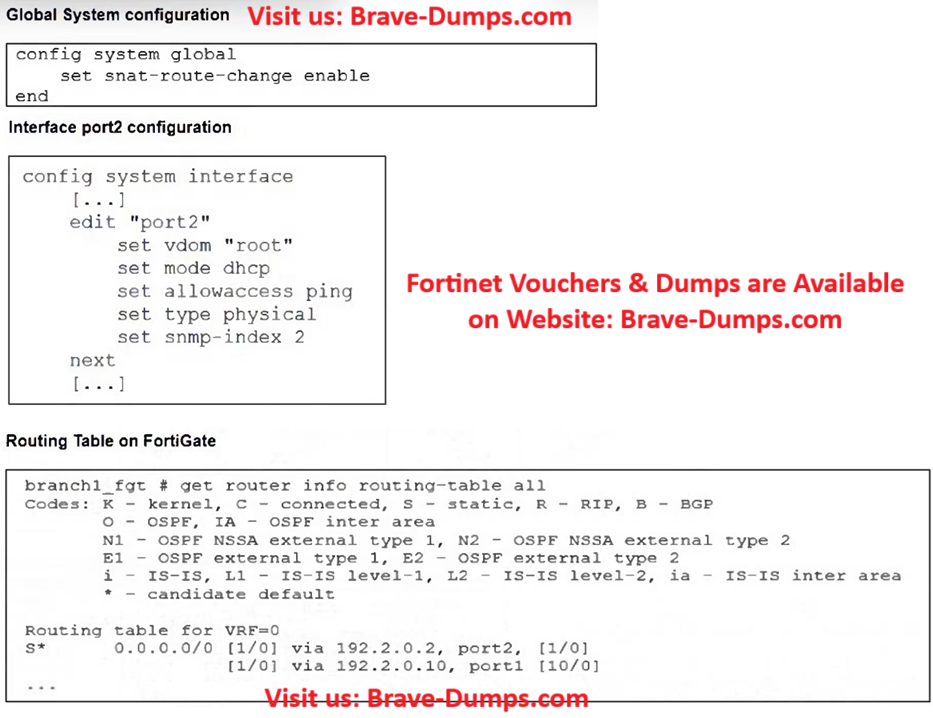
To discuss, my own understanding :The Trigger: Because snat-route-change is enabled, FortiGate is told: "If any routing configuration changes, I need to double-check my existing SNAT sessions." The "Dirty" Flag: FortiGate flags the sessions on port2 as dirty. This doesn't kill the session; it just marks it for a re-evaluation when the next packet arrives. The Re-evaluation: FortiGate looks at the routing table again.
Port 2: Distance 1
Port 1: Distance 10
The Decision: Since Distance 1 is still strictly better than Distance 10, Port 2 remains the "Best Route." The Priority (20) is never even looked at because the tie was already broken by the Distance. The Result: Traffic stays on Port 2.
Port 2: Distance 1
Port 1: Distance 10
The Decision: Since Distance 1 is still strictly better than Distance 10, Port 2 remains the "Best Route." The Priority (20) is never even looked at because the tie was already broken by the Distance. The Result: Traffic stays on Port 2.
Anonymous User
7 months ago
Selected: A, D
A D
Brave-Dumps.com Admin
7 months ago
please explain your answer.
asa
6 months ago
Selected: A, D
set snat-route-change enable requires to change snat info after the route table get updated
Refer to the exhibits. The administrator increases the member priority on port2 to 20. Upon configuration changes and the receipt of new packets, which two actions does FortiGate perform on existing sessions established over port2? (Choose two answers)
Brave-Dump Community Votes