View all questions & answers for the NSE 6 – SD-WAN 7.6 Enterprise Administrator Exam Materials exam
NSE 6 – SD-WAN 7.6 Enterprise Administrator Exam Materials - Question #69 Discussion
Community Explanations & Comments (3)
Anonymous User
9 months ago
Selected: A, B
Can you please explain why this is A&B? I need some clarification on this question.
Which of these 2 commands "preserve-session route enable & snat-route-change" take precedence?
Theres is another question, which does not have the "preserve-session route enable" and the answer is still the same and I agree.
Which of these 2 commands "preserve-session route enable & snat-route-change" take precedence?
Theres is another question, which does not have the "preserve-session route enable" and the answer is still the same and I agree.
Anonymous User
9 months ago
Selected: D, E
on page 299 SDWAN 7.6 Enterp Admin
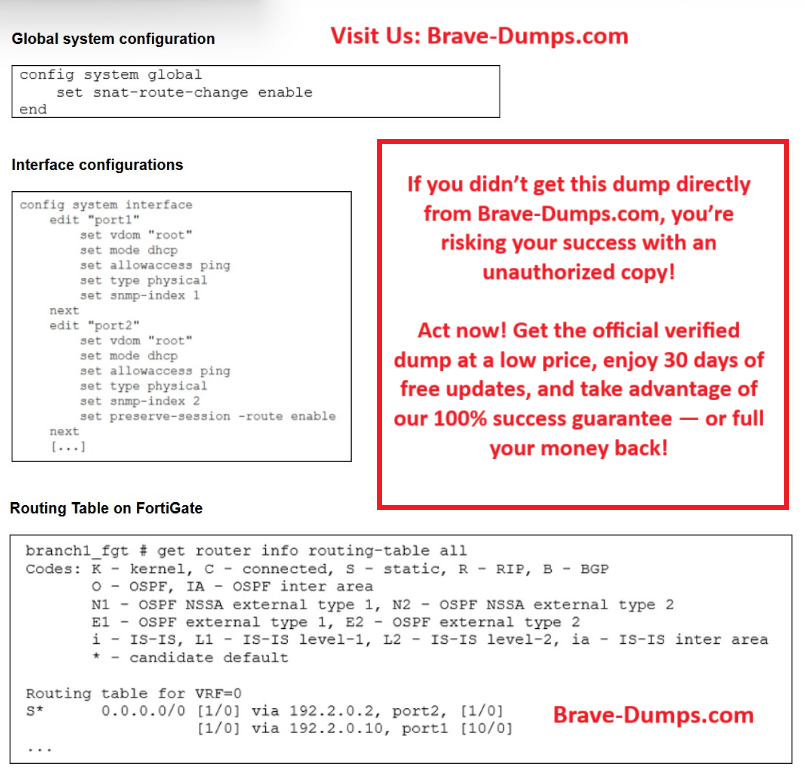
It say's that when you enable 'preserve-session route' the interface stickiness is enabled which means unless that interface is disabled old traffic will still use port 2, and new traffic will use the new outgoing interface port 1.
It say's that when you enable 'preserve-session route' the interface stickiness is enabled which means unless that interface is disabled old traffic will still use port 2, and new traffic will use the new outgoing interface port 1.
Anonymous User
6 months ago
Selected: D, E
A. FortiGate updates the gateway info of SNAT sessions to use port1 instead of port2 ❌
preserve-session-route enable on port2 prevents this — existing sessions stay on port2.
B. FortiGate flags all sessions as dirty ❌
Only SNAT sessions are flagged dirty when snat-route-change is enabled, not all sessions.
C. FortiGate flags SNAT sessions as dirty only if an IP pool is assigned ❌
snat-route-change applies to all SNAT sessions regardless of IP pool — this is incorrect.
D. FortiGate continues routing all existing sessions over port2 ✅
Because preserve-session-route is enabled on port2 AND the route is still valid, existing sessions continue to egress port2.
E. FortiGate routes new sessions over port1 ✅
After the priority change, port1 becomes the preferred path (lower priority value wins; port2 is now 20, port1 default 0/lower). New sessions follow the new best route → port1.
✅ Correct answers: D and E
Refer to the exhibits. The administrator increases the member priority on port2 to 20. Assuming the route egressing port2 is still valid, upon configuration changes and the receipt of new packets. Which two actions does FortiGate perform on existing sessions established over port2? (Choose two answers)
Brave-Dump Community Votes