View all questions & answers for the NSE 7 - Enterprise Firewall 7.6 Administrator Exam Materials exam
NSE 7 - Enterprise Firewall 7.6 Administrator Exam Materials - Question #47 Discussion
Community Explanations & Comments (7)
Fatma Salih
11 months ago
Selected: B
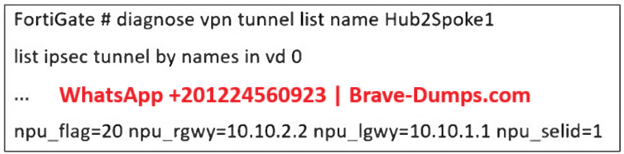
npu_flag=20 = Unsupported cipher
Hasan Ahmed
11 months ago
Selected: B
Correct answer is B
'npu_flag=20'. IPsec SA cannot be offloaded to NPU because either the cipher or the HMAC is not supported by NPU.
'npu_flag=20'. IPsec SA cannot be offloaded to NPU because either the cipher or the HMAC is not supported by NPU.
Shabeeb Kunhipocker
11 months ago
Selected: B
Admin Guide, Page 300
Podb
10 months ago
Selected: B
correct B,
npu_flag=20 = Unsupported cipher
npu_flag=20 = Unsupported cipher
Adam
9 months ago
Selected: B
npu_flag= 00 -> Both IPsec SAs loaded to the kernel
npu_flag= 01 -> Outbound IPsec SA copied to NPU
npu_flag= 02 -> Inbound IPsec SA copied to NPU
npu_flag= 03 -> Both outbound and inbound IPsec SA copied to NPU
npu_flag= 20 -> Unsupported cipher or HMAC, IPsec SA cannot be offloaded
npu_flag= 01 -> Outbound IPsec SA copied to NPU
npu_flag= 02 -> Inbound IPsec SA copied to NPU
npu_flag= 03 -> Both outbound and inbound IPsec SA copied to NPU
npu_flag= 20 -> Unsupported cipher or HMAC, IPsec SA cannot be offloaded
zineeddine Mohamed
7 months ago
Selected: B
page 300
Anonymous User
6 months ago
Selected: B
Enterprise_Firewall_7.6_Administrator_Study_Guide Page 300
Refer to the exhibit, which shows a partial troubleshooting command output. You are using IPsec on FortiGate extensively. Many tunnels are showing information that is similar to the output shown in the exhibit. Which statement about your IPsec use is correct? (Choose one answer)
Brave-Dump Community Votes