View all questions & answers for the NSE 7 - Enterprise Firewall 7.6 Administrator Exam Materials exam
NSE 7 - Enterprise Firewall 7.6 Administrator Exam Materials - Question #53 Discussion
Community Explanations & Comments (7)
Anonymous User
9 months ago
Selected: A, D
I don't think this needs to be a fortilink interface
Adam
9 months ago
Selected: C, D
From Study Guide:
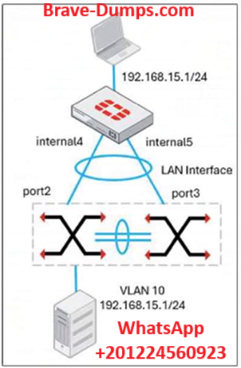
You can connect FortiGate to a single FortiSwitch using an aggregate interface. However, using Multichassis Link Aggregation (MCLAG) with multiple FortiSwitch devices enhances layer 2 redundancy, allowing two FortiSwitch devices to act as one unit.
Both scenarios typically use FortiLink with a standard 802.3ad protocol to connect the firewall and switches.
https://docs.fortinet.com/document/fortiswitch/7.6.4/fortilink-guide/173292/configuring-stp-settings
STP is not supported between a FortiGate unit and a FortiSwitch unit in FortiLink mode.
802.3ad (LACP Link Aggregation) without MCLAG won't work as both FortiSwitches are not a cluster yet
MCLAG works with FortiSwitches, not SDWAN
Anonymous User
7 months ago
Selected: C, D
C and D, Adam is right with his elaborations, study guide p.62
Anonymous User
7 months ago
Selected: A, D
Where arethe information aabout fortilink interface using?
Anonymous User
7 months ago
Selected: C, D
Fortigate devices run fortilink with downstream switches. The links are bundled so they must be using LACP for MCLAG.
Anonymous User
6 months ago
Selected: C, D
Enterprise_Firewall_7.6_Administrator_Study_Guide page 62
Anonymous User
5 months ago
Selected: C, D
Enterprise_Firewall_7.6_Administrator_Study_Guide page 62 (Both scenarios typically use FortiLink with a standard 802.3ad protocol to connect the firewall and switches)
Refer to the exhibit. A LAN interface connected from FortiGate to two FortiSwitch devices is shown. Which two statements about the LAN interface connection shown in the exhibit are correct? (Choose two answers)
Brave-Dump Community Votes