View all questions & answers for the NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials exam
NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials - Question #11 Discussion
Community Explanations & Comments (1)
javaughn Bryan
11 months ago
Selected: B, C
The ZTNA server defines the access proxy VIP and the real servers that clients connect to. The firewall policy matches and redirects client requests to the access proxy VIP. You can also enable authentication.
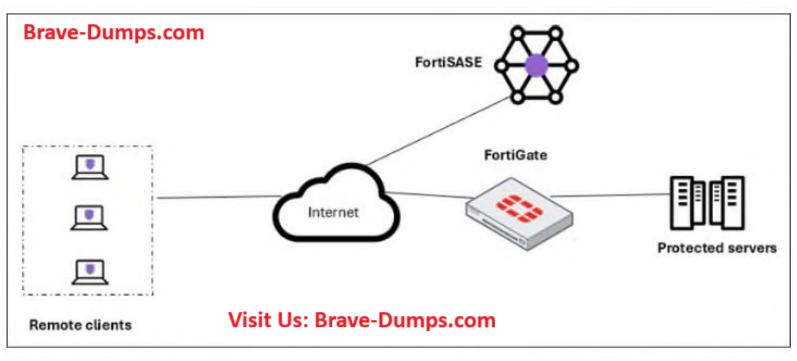
A TCP forwarding access proxy (TFAP) is configured to demonstrate an HTTPS reverse proxy that forwards TCP traffic to the designated resource. The access proxy tunnels TCP traffic between the client and FortiGate over HTTPS, and forwards the TCP traffic to the protected resource. It verifies user identity, device identity, and trust context, before granting access to the protected source.
PAGE: PAGE 53&55 SASE ENTERPRISE GUIDE
A customer needs to implement device posture checks for their remote endpoints while accessing the protected server. They also want the TCP traffic between the remote endpoints and the protected servers to be processed by FortiGate. In this scenario, which two setups will achieve these requirements? (Choose two answers)
Brave-Dump Community Votes