View all questions & answers for the NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials exam
NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials - Question #38 Discussion
Community Explanations & Comments (2)
Brave-Dumps.com Admin
11 months ago
Selected: C
C is correct.
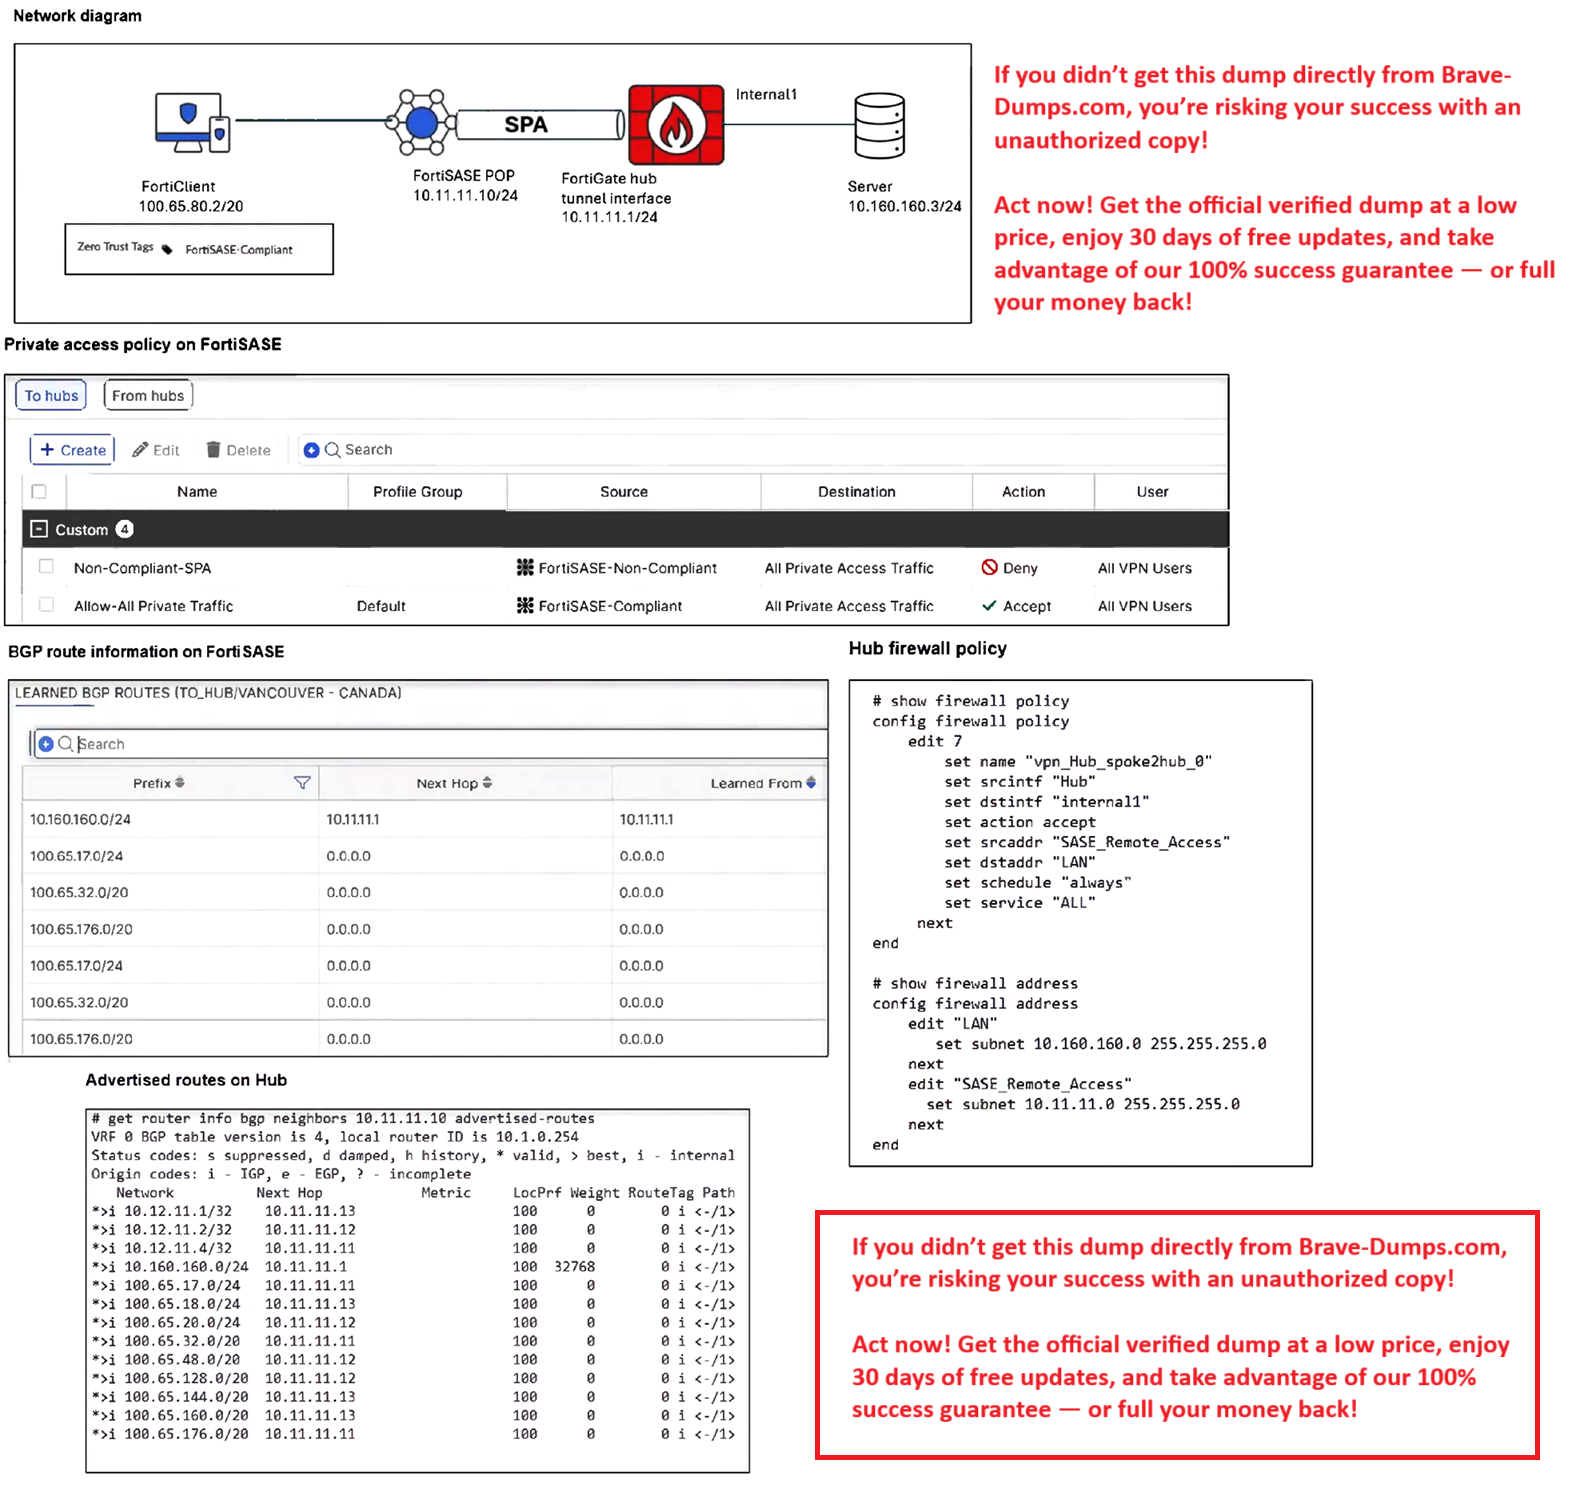
FortiSASE routing table appear a network 10.160.160.0/24 learned from Fortigate Hub 10.11.11.1 but in Firewall policy object dont have a address 100.65.80.0/24
FortiSASE routing table appear a network 10.160.160.0/24 learned from Fortigate Hub 10.11.11.1 but in Firewall policy object dont have a address 100.65.80.0/24
javaughn Bryan
11 months ago
Selected: C
C is indeed correct. The server subnet is there but not the FortiClient IP address because it was not configured in the Firewall Policy. See, the Firewall sits between the FortiSASE and the intended Server, but it also needs to see and be allowed on the FortiClient network (which it can't see now because it was not configured). So FortiSASE can see the server that was advertised by the FortiGate, but the endpoint behind FortiSASE is unable to access said server because its LAN is not in the Firewall policy, thus being blocked from ever reaching the server.
Refer to the exhibits. A FortiSASE administrator has configured FortiSASE as a spoke to a FortiGate hub. The tunnel is up to the FortiGate hub. However, the remote FortiClient is not able to access the web server hosted behind the FortiGate hub. What is the reason for the access failure? (Choose one answer)
Brave-Dump Community Votes