View all questions & answers for the NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials exam
NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials - Question #7 Discussion
Community Explanations & Comments (8)
Brave-Dumps.com Admin
1 year ago
Selected: A, B
it needs additional check.
javaughn Bryan
11 months ago
Selected: A, B
This is agentless so no need for FortiClient and SSO doesn't really apply here. This question is purely about application access. Since it's agentless... an ZTNA application gateway is need and a SPA tunnel also
Anonymous User
8 months ago
Selected: B, D
Agentless means proxy
Anonymous User
7 months ago
Selected: A, D
FortiSASE Agentless ZTNA (Does NOT require FortiGate App Gateway). The heavy lifting moves to the cloud. The user logs into the FortiSASE web portal. The FortiSASE cloud itself acts as the proxy and the gateway.
Here is the exact flow:
The user authenticates to the FortiSASE portal (using proxy SSO).
FortiSASE verifies their identity and permissions.
FortiSASE proxies the connection and sends the already-authorized traffic down the standard Secure Private Access (SPA) IPsec tunnel to your branch FortiGate.
The FortiGate receives this traffic over the tunnel and simply routes it to the internal server like normal network traffic.
Because FortiSASE handles the proxying and the gateway duties in the cloud, your on-premise FortiGate just acts as a standard router/firewall for that traffic. No ZTNA Application Gateway configuration is needed on the FortiGate itself for Agentless ZTNA.
I Am Weird
7 months ago
Selected: A, D
AD
mahmoud mostafa
6 months ago
Selected: A, D
AD is correct answer
this is agenless access so no forticlient and authentication is via SWG SSO (mostly with SAML)
And with the user authenticated, FortiSASE Gives it the Access accordingly SPA Configuration
page 173: FortiSASE 25 Administrator Study Guide
this is agenless access so no forticlient and authentication is via SWG SSO (mostly with SAML)
And with the user authenticated, FortiSASE Gives it the Access accordingly SPA Configuration
page 173: FortiSASE 25 Administrator Study Guide
Matthias Strauß
6 months ago
Selected: A, D
A & D
https://docs.fortinet.com/document/fortisase/latest/feature-administration-guide/329570/agentless-ztna
https://docs.fortinet.com/document/fortisase/latest/feature-administration-guide/329570/agentless-ztna
Anonymous User
4 months ago
Selected: A, D
pagina 81 de guia de estudio lo indica como prerequisito
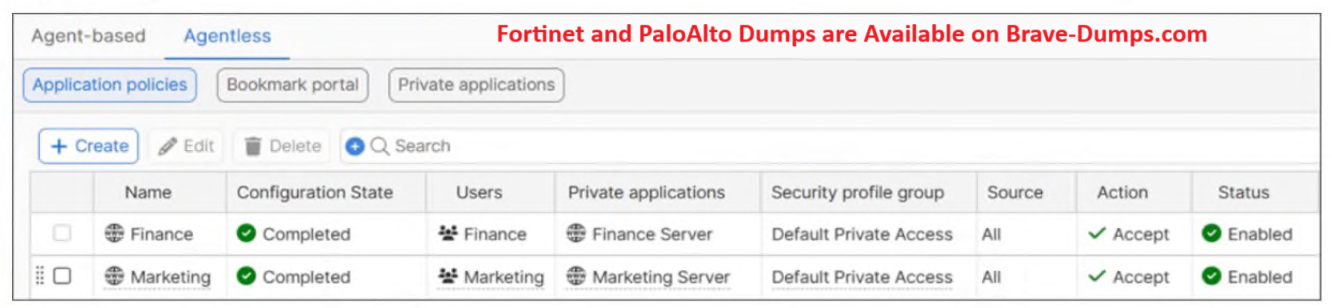
Refer to the exhibit. Which two prerequisites must be met to use the feature shown in the exhibit? (Choose two answers)
Brave-Dump Community Votes