View all questions & answers for the NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials exam
NSE 7 - FortiSASE 25 Enterprise Administrator Exam Materials - Question #8 Discussion
Community Explanations & Comments (6)
Brave-Dumps.com Admin
1 year ago
Selected: D
it needs additional check
javaughn Bryan
11 months ago
Selected: C
ANSWER IS C.
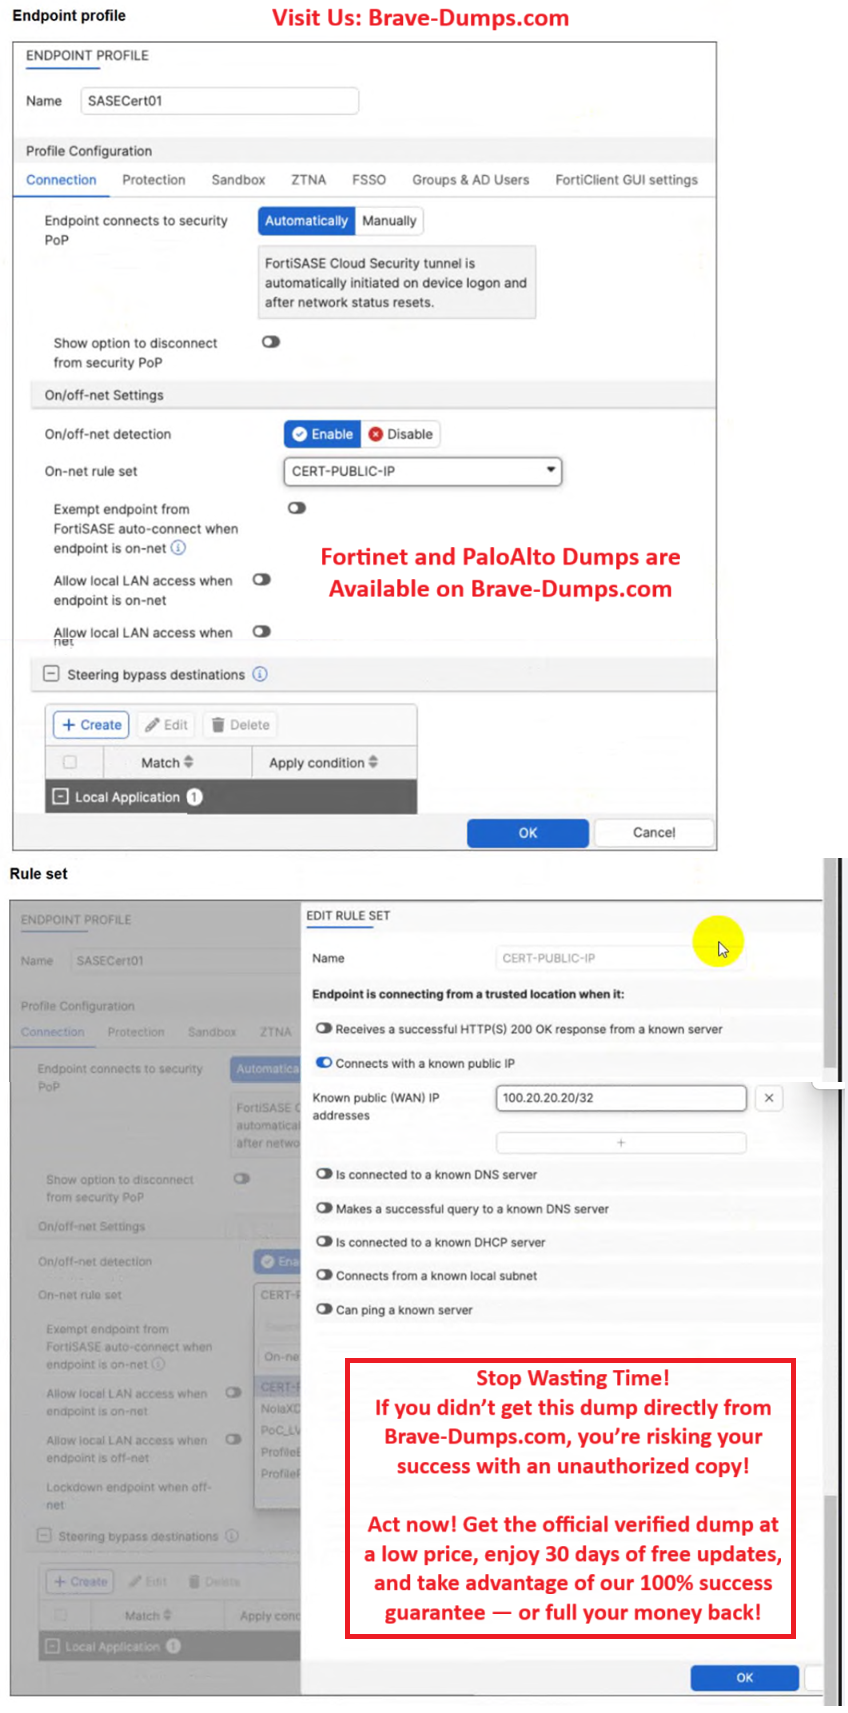
FortiSASE auto-connect can be exempted of detected on-net.
NSE7 STUDY GUIDE
PAGE 88
FortiSASE auto-connect can be exempted of detected on-net.
NSE7 STUDY GUIDE
PAGE 88
Brave-Dumps.com Admin
11 months ago
Thank you.
Brave-Dumps.com Admin
11 months ago
Selected: C
C is the correct
Anonymous User
7 months ago
Selected: C
C
I Am Weird
6 months ago
Selected: C
C
JAVIER KAMANEL
6 months ago
Selected: C
The answer is C , when you configure the on-net rule you must enable exempt Sase from automatically connect when on net …
A customer configured the On/off-net detection rule to disable FortiSASE VPN auto-connect when users are inside the corporate network. The rule is set to Connects with a known public IP using the company’s public IP address. However, when the users are on the corporate network, the FortiSASE VPN still auto-connects. The customer has confirmed that traffic is going to the internet with the correct IP address. Which configuration is causing the issue? (Choose one answer)
Brave-Dump Community Votes