View all questions & answers for the NSE 7 - Public Cloud Security 7.6.4 Architect Exam Materials exam
NSE 7 - Public Cloud Security 7.6.4 Architect Exam Materials - Question #40 Discussion
Community Explanations & Comments (1)
Mr_Fortitito
1 year ago
Selected: C
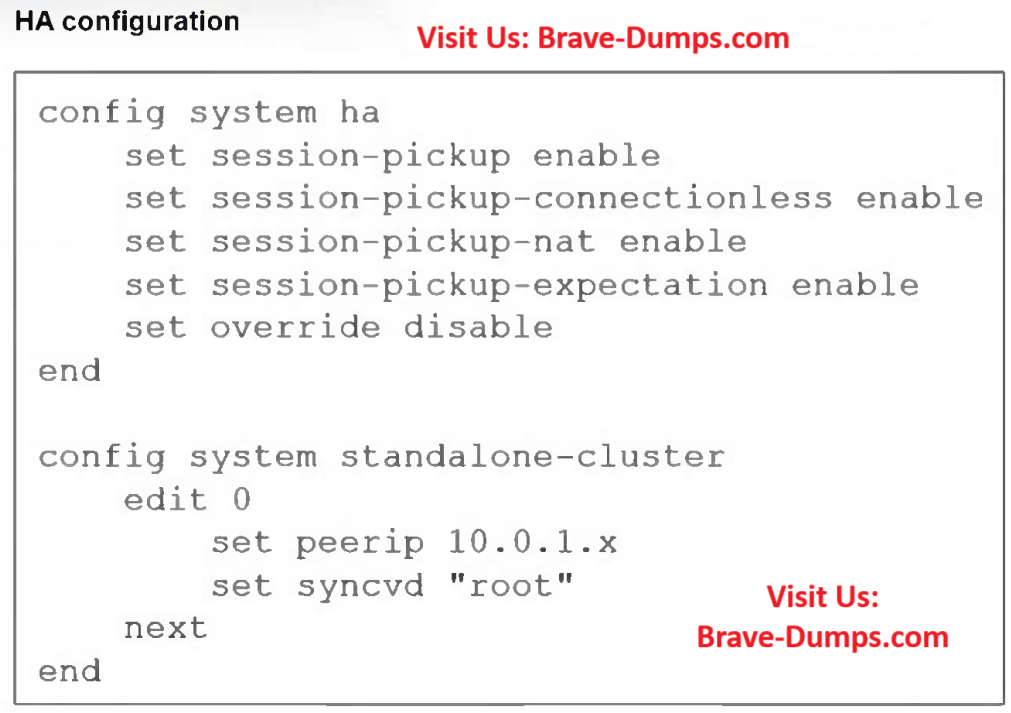
Page 93 study guide, For port 2, which connects to the internal load balancer, the peer IP must be configured as the port 2 IP address of the other FortiGate unit. This configuration ensures that both internal interfaces can directly exchange information, enabling proper session synchronization. Such synchronization is essential in an active-active cluster, as it guarantees that ongoing sessions remain uninterrupted even if a failover event occurs.
Refer to the exhibit. You deployed an HA active-active load balance sandwich with two FortiGate VMs in Microsoft Azure. After the deployment, you prefer to use FGSP to synchronize sessions, and allow asymmetric return traffic. In the environment, FortiGate port 1 and port 2 are facing external and internal load balancers respectively. What IP address must you use in the peerip configuration? (Choose one answer)
Brave-Dump Community Votes