View all questions & answers for the NSE 7 - Public Cloud Security 7.6.4 Architect Exam Materials exam
NSE 7 - Public Cloud Security 7.6.4 Architect Exam Materials - Question #62 Discussion
Community Explanations & Comments (2)
alex silva
1 year ago
Selected: B, C, D
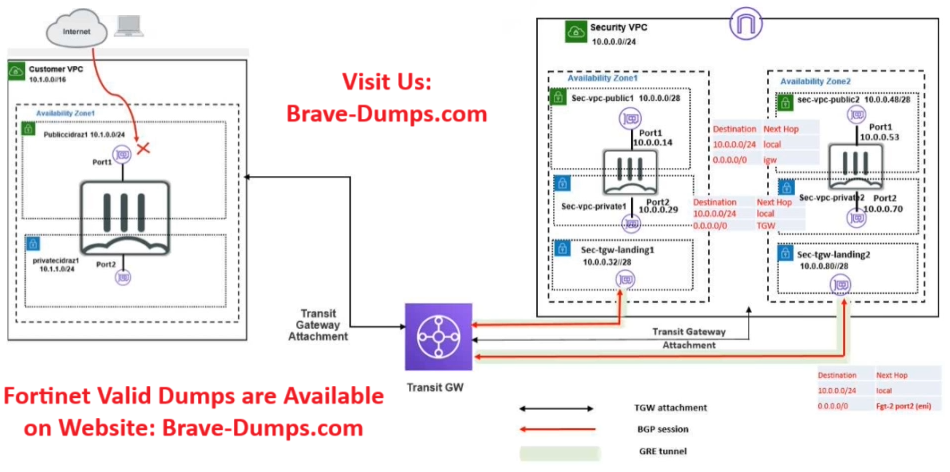
There is no way it can be A, you do not associate an EIP with an entire subnet, but rather with a specific network interface (ENI), which in this case is port 1 on the FortiGate.
And C, ensures that the return route for incoming traffic is established, allowing the HTTPS connection to succeed.
B, C and D
And C, ensures that the return route for incoming traffic is established, allowing the HTTPS connection to succeed.
B, C and D
Anonymous User
1 week ago
Selected: B, D, E
I prefer answer E over C: I want my public (admin) IP address to be routed though the internet gateway rather then the TGW. Otherwise return traffic is routed via Security VPC which would result in asymmetric routing.
Refer to the exhibit. In your Amazon Web Services (AWS), you must allow inbound HTTPS access to the Customer VPC FortiGate VM from the internet. However, your HTTPS connection to the FortiGate VM in the Customer VPC is not successful. Also, you must ensure that the Customer VPC FortiGate VM sends all the outbound Internet traffic through the Security VPC. How do you correct this issue with minimal configuration changes? (Choose three answers)
Brave-Dump Community Votes