View all questions & answers for the NSE 7 - Secure Networking 7.6 Architect Exam Materials exam
NSE 7 - Secure Networking 7.6 Architect Exam Materials - Question #1 Discussion
Community Explanations & Comments (5)
Md Nasir Uddin
2 months ago
Selected: B, C
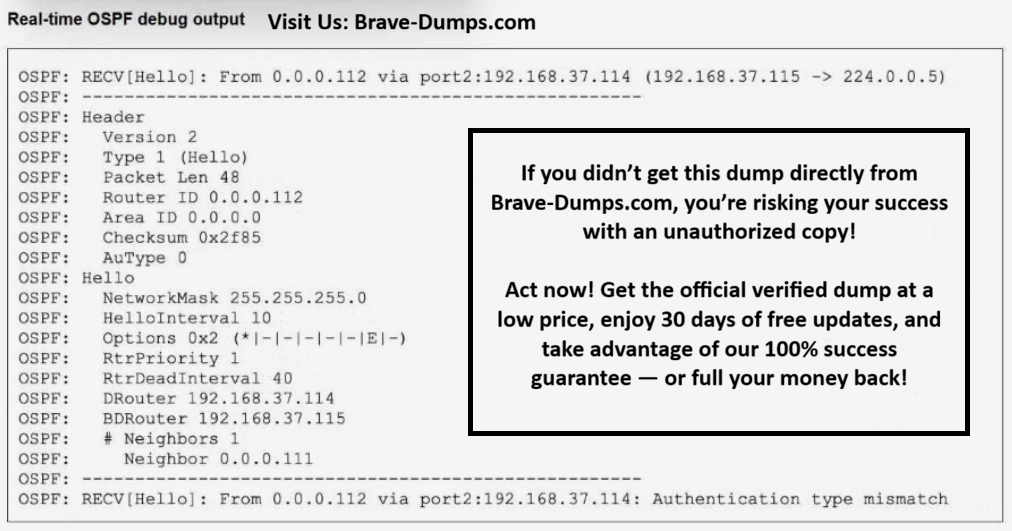
Authentication configuration mismatch. Neigbour routter does not configure any authuntication showing authTpe 0 mean no cleartext or MD5 configured
marek Marucha
1 month ago
Selected: A, C
Remote Peer Configuration: In the header section of the received Hello packet, the field AuType is listed as 0 (Null/No authentication), while the error message indicates a mismatch. This means the remote peer (0.0.0.112) sent a Hello packet with no authentication (AuType 0), whereas the local Fortigate receiving the packet expects OSPF cleartext (AuType 1) or MD5 (AuType 2) authentication, or vice versa—meaning the remote peer is sending authentication (cleartext/MD5) while the local side expects none, or the remote sent cleartext/MD5 (AuType 1 or 2) and the local side has none or a different type configured (Option A).
Luis
1 month ago
Selected: B, C
Remote peer (0.0.0.112) send null (no authentication) in hello packet, and local FGT debug shows "auth type mistmach"; so local FGT expects Cleartext (autype 1) or MD5 (autype 2).
Anonymous User
3 weeks ago
Selected: B, C
ans B and C
Kurt Richter
1 day ago
Selected: B, C
The last line of the OSPF header from the neighbor indicates AuType = 0 which designates no authentication. This means A is wrong. The last line of the output clearly indicates an authentication mismatch (answer C). Therefore, since the remote peer is not expecting authentication, the local peer must be configured for authentication (whether MD5 or cleartext).
Refer to the exhibit. Partial output of a real-time OSPF debug is shown. Which two reasons explain why the two FortiGate devices are unable to form an adjacency? (Choose two answers)
Brave-Dump Community Votes