View all questions & answers for the NSE 7 - Secure Networking 7.6 Architect Exam Materials exam
NSE 7 - Secure Networking 7.6 Architect Exam Materials - Question #27 Discussion
Community Explanations & Comments (5)
Anonymous User
1 month ago
Selected: A, B
yes
Anonymous User
1 month ago
Selected: A, B
Correct.
Flag20
1 week ago
Selected: A, C
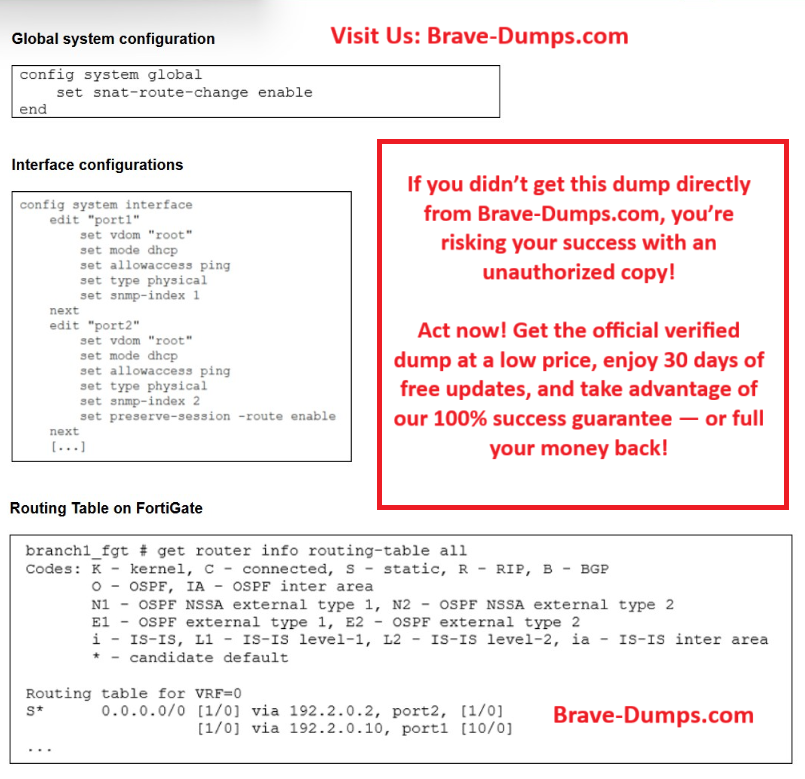
Port2 is the active default route (priority 1 vs 10 on port1). Raising its member priority to 20 makes port1 the preferred route, so the routing table changes.
A is correct: on a route change, FortiGate flags existing sessions as dirty so they are re-evaluated when new packets arrive.
C is correct: preserve-session-route is enabled on port2, and the route egressing port2 is still valid. Existing sessions therefore keep being routed over port2, while only new sessions use port1.
Jean_Teub
4 days ago
Selected: A, C
Preserve route
Kurt Richter
1 day ago
Selected: A, C
because of the "preserve-session-route" command, all existing sessions will NOT reroute over port1 -- they will continue to route over port 2 as long as the 0/0 route through port2 remains valid. These sessions will be marked "dirty" due to the routing update.
Refer to the exhibits. The administrator increases the member priority on port2 to 20. Assuming the route egressing port2 is still valid, upon configuration changes and the receipt of new packets. Which two actions does FortiGate perform on existing sessions established over port2? (Choose two answers)
Brave-Dump Community Votes