View all questions & answers for the NSE 7 - Security Operations 7.6 Architect Materials exam
NSE 7 - Security Operations 7.6 Architect Materials - Question #32 Discussion
Community Explanations & Comments (3)
Anonymous User
7 months ago
Selected: B, C
BC
Brave-Dumps.com Admin
6 months ago
Why?
Anonymous User
6 months ago
Selected: B, D
Answer: B and D
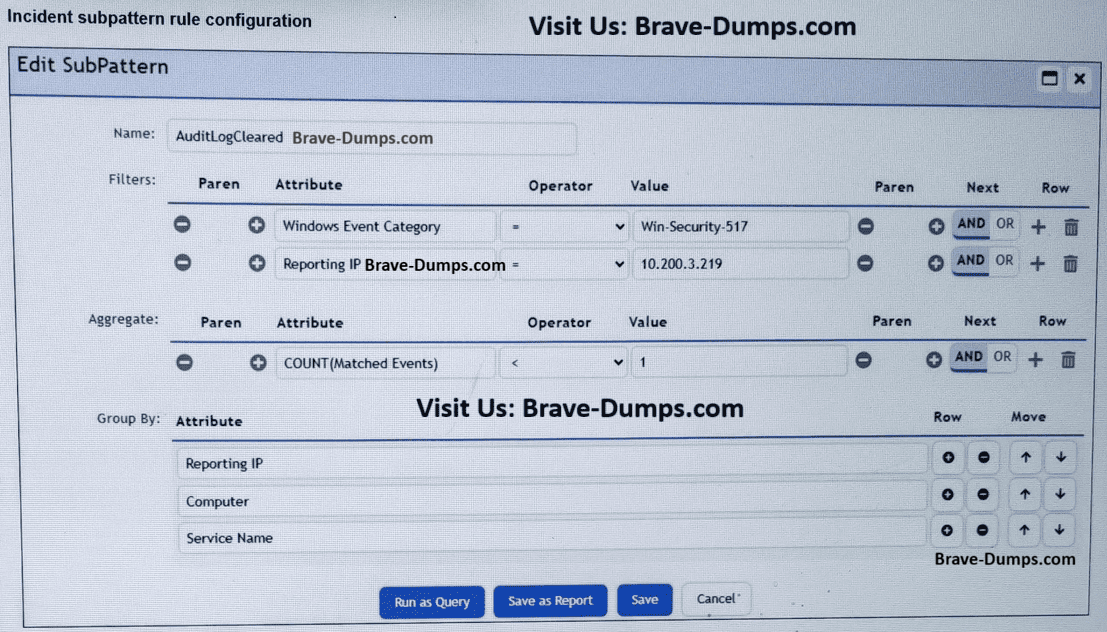
B — The aggregate operator is incorrect.
COUNT(Matched Events) < 1 triggers when zero events match, which is the opposite of what you need for detecting audit log clearing. It should be >= 1.
D — The mandatory Event Type attribute is missing.
The filter uses "Windows Event Category" but does not include the Event Type attribute, which is the standard and required attribute in FortiSIEM subpattern filters for identifying events. All rule examples in the official study guide use Event Type as the primary filter attribute.
Why not A: The time window is configured at the rule level, not inside the subpattern — so it's not missing from this view.
Why not C: Reporting IP, Computer, and Service Name are valid, non-conflicting Group By attributes.
Brave-Dumps.com Admin
6 months ago
Selected: B, D
B, D
Refer to the exhibit. What are the two mistakes in the incident subpattern rule configuration? (Choose two answers)
Brave-Dump Community Votes