View all questions & answers for the NSE 7 - Security Operations 7.6 Architect Materials exam
NSE 7 - Security Operations 7.6 Architect Materials - Question #59 Discussion
Community Explanations & Comments (3)
Simon Cliffe
8 months ago
Selected: C, D
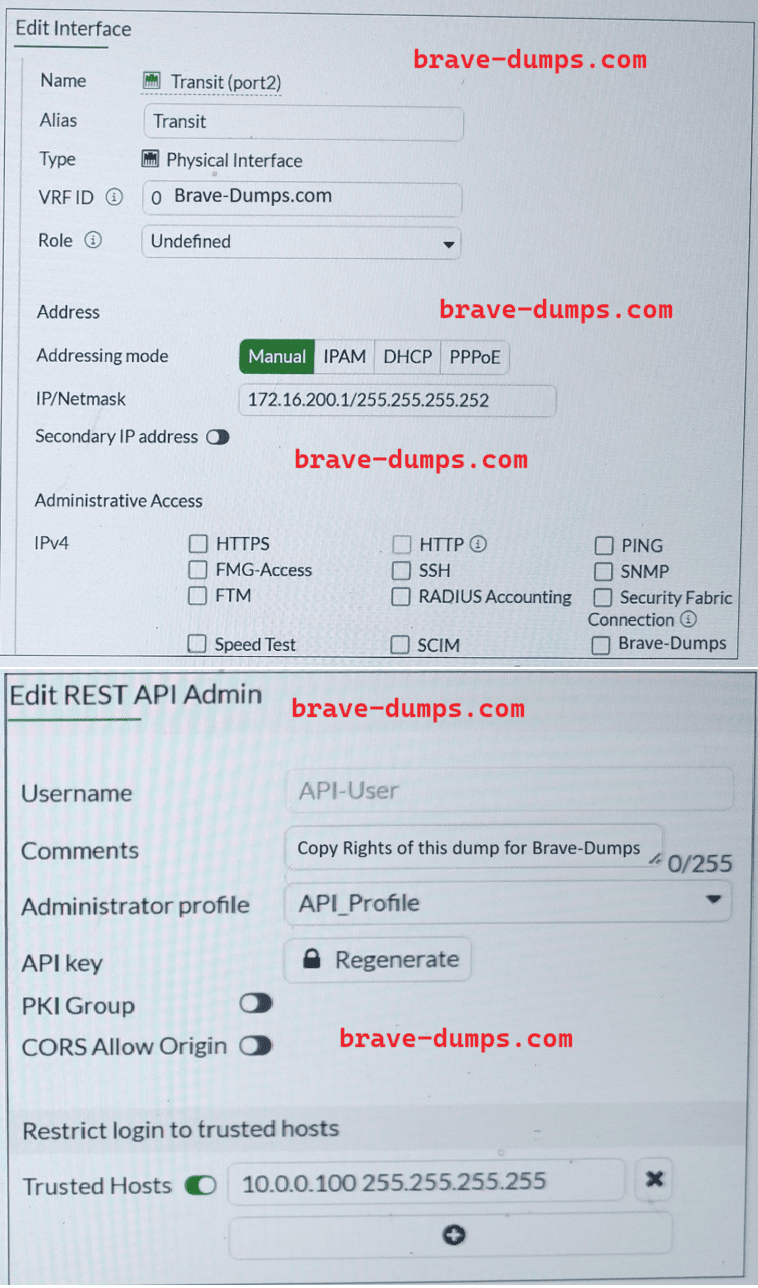
Fortinet 1 – C & D – Reason – Trusted hosts is optional, not required, the SOAR talks to a standard REST API, not custom.
Anonymous User
7 months ago
Selected: C, D
CD
Anonymous User
6 months ago
Selected: A, D
Trusted hosts is enabled on the API administrator, so the FortiSOAR IP must be added to the list. Also, HTTPS must be enabled on the FortiGate interface as a local-in policy requirement. Both are FortiGate-side prerequisites, making them the valid causes for the connection failure.
Refer to the exhibits. You configured the FortiGate connector on FortiSOAR. You want to allow FortiSOAR (10.200.200.160) to perform actions on FortiGate (172.16.200.1). However, the connection attempt fails. Assume that the FortiGate connector is configured correctly on the FortiSOAR side. Which two configurations are required on FortiGate? (Choose two answers)
Brave-Dump Community Votes