View all questions & answers for the NSE 8 - Recertification Exam (813) Materials exam
NSE 8 - Recertification Exam (813) Materials - Question #89 Discussion
Community Explanations & Comments (4)
Sergio Hernandez
1 year ago
Selected: B, C
b,c are the two answers
Mohamed laamouri
10 months ago
Selected: B, D
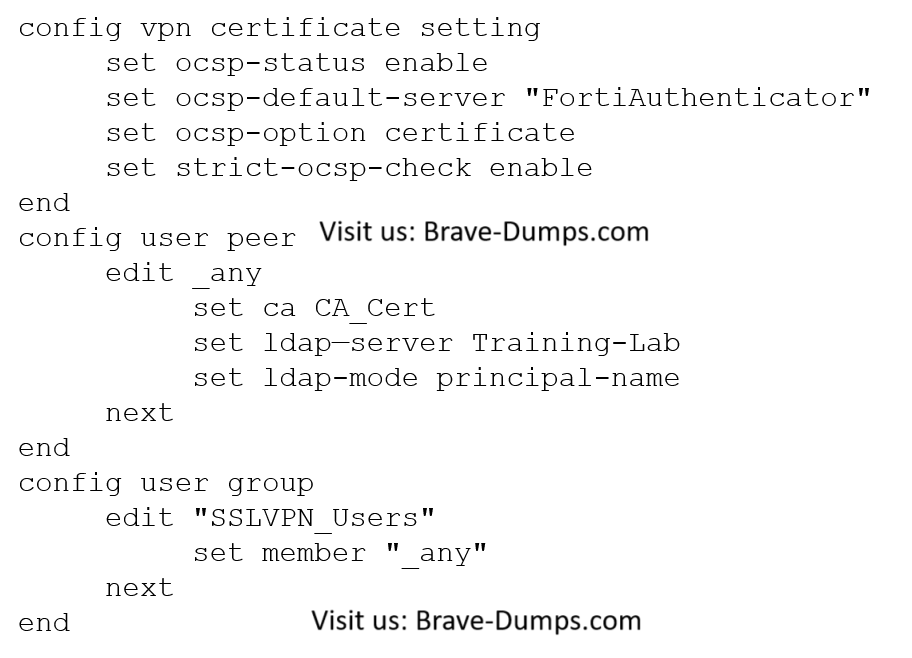
set strict-ocsp-check enable signifie que la vérification OCSP est stricte :
→ Si le serveur OCSP est inaccessible, l’authentification échoue (donc C serait normalement faux).
En mode strict, FortiGate ne fait pas de fallback sur la CA.
Si strict-ocsp-check était désactivé, alors C serait vrai (authentification réussit si le certificat correspond à la CA).
Mais ici, il est activé.
Donc, selon la configuration affichée, les bonnes réponses sont B et D.
boss123
10 months ago
Selected: C, D
I would say CD... OSCP will not go to FortiAuthentication because OCSP option is set to certificate not server. OSCP will use URL on the certificate
Brave-Dumps.com Admin
10 months ago
Selected: B, D
B,D
An administrator has configured a FortiGate device to authenticate SSL VPN users using dogotal certificates. A FortiAuthenticator is the certificate authority (CA) and the Online Certificate Status Protocol (OCSP) server. Part of the FortiGate configuration is shown below: Based on this configuration, which two statements are true? (Choose two answers)
Brave-Dump Community Votes