View all questions & answers for the NSE I - OT Security 7.6 Architect Exam Materials exam
NSE I - OT Security 7.6 Architect Exam Materials - Question #62 Discussion
Community Explanations & Comments (5)
Brave-Dumps.com Admin
6 months ago
Selected: C
C
FG got the patching vulnerabilities for the devices
FG got the patching vulnerabilities for the devices
İsmail Ürek
6 months ago
Selected: B
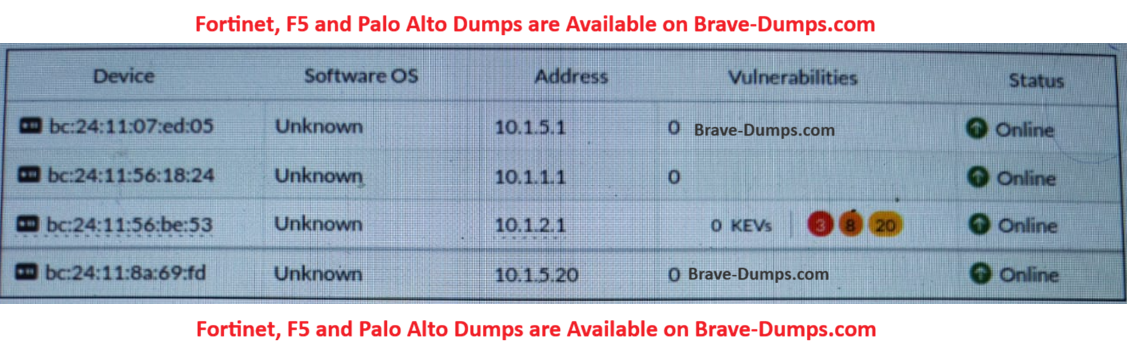
Reason: For vulnerability information (such as critical and high-risk counts) related to devices to appear in the Asset Identity List on the FortiGate interface, the “Virtual Patching” profile must be enabled in the rule that monitors traffic. FortiGate queries FortiGuard via MAC addresses only through this profile, identifies device-specific vulnerabilities, and lists them on this screen. Other security profiles, such as antivirus or IPS, do not provide this specific vulnerability mapping.
Anonymous User
4 months ago
Selected: C
Look C is right
Ahmed Talaat
2 months ago
Selected: B
to have the details in screenshot, need virtual patching profile
Ludovic Peny
2 months ago
Selected: B
I also think B is the right answer - the vulnerabilities details are shown thanks to this feature
Refer to the exhibit. Which statement about this partial Asset Identity List page is correct? (Choose one answer)
Brave-Dump Community Votes